

oSIST prEN 18235-3:2026
(Main)Trusted data transactions - Part 3: Interoperability requirements
- Abstract
This document specifies requirements and guidance for the interoperability of data, data sharing mechanisms, and services within data spaces. It covers requirements, criteria and implementation guidance on:
- dataset content, use restrictions, licences, data collection methodology, data quality and uncertainty, and on machine-readable formats to find, access and use of data;
- data structures, data formats, vocabularies, classification schemes, taxonomies and code lists, and how to describe these elements a publicly available and consistent manner;
- technical means to access the data, such as application programming interfaces, and their terms of use and quality of service to enable automatic access and transmission of data between parties;
- where applicable, the means to enable the interoperability of tools for automating the execution of data sharing contracts.
This document is applicable to all organizations participating in dataspaces, regardless of their size or type.
- Status
- Not Published
- Public Enquiry End Date
- 31-Jul-2026
- Technical Committee
- I11 - Imaginarni 11
- Current Stage
- 4020 - Public enquire (PE) (Adopted Project)
- Start Date
- 03-Jun-2026
- Due Date
- 21-Oct-2026
- Completion Date
- 03-Aug-2026
oSIST prEN 18235-3:2026 is a draft European Standard from CEN on trusted data transactions. It specifies interoperability requirements for data, data sharing mechanisms, and services within data spaces, so organizations can describe data products, expose them through catalogues and interfaces, and automate data-sharing contracts in a consistent way. It applies to all organizations participating in dataspaces, regardless of size or type.
What does oSIST prEN 18235-3:2026 specify?
oSIST prEN 18235-3:2026 sets requirements and guidance for interoperability in data spaces. It focuses on how participants identify parties and objects, describe data products, publish metadata, describe data models, control access, and negotiate and execute data sharing contracts.
The document is organized into clauses on scope, normative references, terms and definitions, an overview, general requirements, data product description, data model description, data access, and automated negotiation and execution of data sharing contracts.
| Annex | What it covers |
|---|---|
| Annex A | Implementation of interoperability requirements, with approaches and examples |
| Annex ZA | Relationship between this European Standard and Regulation (EU) 2023/2854 Article 33 |
What are the key requirements of oSIST prEN 18235-3:2026?
oSIST prEN 18235-3:2026 turns interoperability into a set of practical rules for identifiers, metadata, access, and contract handling. In practice, this means a data provider cannot just offer data - it has to publish enough machine-readable information for a data user to find, interpret, access, and govern that data.
Identifiers, claims, and data sharing contracts
Clause 5.2 requires globally unique identifiers for entities and objects that are referenced by multiple parties or services. When a globally unique scheme is used, the identifier shall be a URI. This matters because shared data spaces depend on unambiguous references to participants, data products, and contracts.
Clause 5.2 also requires claims to be machine readable, verifiable through a trust service, and aligned with an agreed ontology in the trust framework. The standard covers claims about the represented party, data space participation, and granted data rights. In practice, participant agents need to be able to prove who they act for, whether a party belongs to a data space, and what rights have been granted for a specific data product.
Data sharing contracts must also be identified globally and must refer to the data products they cover. Clause 5.3 requires participant agents to support issuing, validating, presenting, and verifying the relevant claims, and to provide a way to initiate, negotiate, and record the contract.
Data product description and publication
Clause 6.2 requires a data provider to document the content of the offered data product. The documentation must include the content description and the applicable use restrictions and licence terms, and should also include data collection methodology, data quality, and uncertainty.
Metadata shall be made accessible through a catalogue service endpoint, and discovery services are used to find catalogue services. This is important because data users first need to find the product and then decide whether the access conditions fit their purpose.
Clause 6 also requires the content to be described with a title and description. If the data space rulebook defines additional attributes, they must be included in the metadata. Any obligations, permissions, and prohibitions for use must be stated in a way that can be verified by claims.
Data model description
Clause 7.2 requires metadata about the structure and format of the data. When semantic models, classification schemes, taxonomies, or code lists apply, the provider must identify them and provide service endpoints where they can be accessed.
This matters because a user needs to know not only what the data is, but how to interpret it. Clause 7 makes semantic compatibility part of the published metadata, which helps avoid integration errors and misinterpretation between systems.
Data access, service levels, and security
Clause 8.2 requires the provider to specify the service endpoint or endpoints for data access and the terms of use for each endpoint. The metadata must also state the nature of the data transmission, such as continuous, bulk download, or real time.
For structured interfaces such as APIs, the metadata must point to documentation for the interface. Clause 8.2.5 requires structured service level agreement metadata, and Clause 8.2.6 requires the required security mechanisms for each endpoint. In practice, this means users can compare service performance, availability, protection rules, and access conditions before starting a transaction.
Automated negotiation and execution
Clause 9.2 requires a structured negotiation capability for data sharing contracts. A data user can initiate a contract request with the required claims, and the provider finalizes the contract once both sides agree. The lifecycle states are Offered, Aborted, Agreed, and Terminated.
After agreement, the provider must notify the user that the data product is accessible, and both parties must inform each other about suspension, completion, or termination of sharing. Clause 9.2.3 also requires the provider to retain a copy of the contract for legal compliance, with optional storage by the user or a third party.
What terms does oSIST prEN 18235-3:2026 define?
- Identifier - A language-independent label, sign, or token that uniquely identifies an object within an identification scheme.
- URI - A compact sequence of characters that identifies an abstract or physical resource.
- Semantic model - A specification of the meaning of concepts, relationships, and constraints in a domain, independent of data structures or formats.
- Participant agent - An agent used to conduct activities in a data space on behalf of a participant.
- Claim - A statement that something is true, including any associated conditions and limitations.
- Data space rulebook - The governance framework for a data space, including principles, processes, standards, protocols, rules, and practices.
- Service endpoint - The web location where a service can be accessed.
- Data sharing contract - The recorded agreement between a data provider and a data user that sets the conditions for data access and use.
Who uses oSIST prEN 18235-3:2026?
oSIST prEN 18235-3:2026 is used by organizations that participate in dataspaces and by the systems that support them. The main practical users are data providers, data users, data rights holders, and the teams building participant agents, trust services, catalogue services, and discovery services.
It is relevant where data is shared across organizational boundaries and must be governed through policies, claims, metadata, and automated contract handling. The introduction links this to research, decision-making, new products and services, and to environments shaped by IoT, cloud-edge computing, wireless networking, and AI.
Which standards are used with oSIST prEN 18235-3:2026?
EN 18235-1 provides the terminology, concepts, and mechanisms used throughout this part. prEN 18235-2 provides the trustworthiness requirements that this part builds on, and Annex ZA states that full coverage of the Data Act interoperability requirements is achieved in combination with EN 18235-2.
Annex A also points to implementation technologies and profiles used in practice, including W3C Decentralized Identifiers, RDF, ODRL, Verifiable Credentials, JWT, OID4VC, and the Eclipse Dataspace Protocol, as examples of how a data space can realize the requirements.
What does the oSIST prEN 18235-3:2026 document contain?
The document combines general concepts with concrete interoperability requirements for the full data-sharing workflow. It covers how to represent identity and claims, how to publish metadata in catalogues, how to describe data structures and semantics, how to expose access endpoints, and how to negotiate and track a data sharing contract.
Each technical clause ends with evaluation criteria that show what participant agents and supporting services should be able to do. Annex A gives implementation-oriented guidance and examples for identifiers, data model descriptions, terms of use, claims, and automated communication. Annex ZA maps the standard to Article 33 of Regulation (EU) 2023/2854 and explains the intended relationship to EU law.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.

DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
oSIST prEN 18235-3:2026 is a draft published by the Slovenian Institute for Standardization (SIST). Its full title is "Trusted data transactions - Part 3: Interoperability requirements". This standard covers: This document specifies requirements and guidance for the interoperability of data, data sharing mechanisms, and services within data spaces. It covers requirements, criteria and implementation guidance on: - dataset content, use restrictions, licences, data collection methodology, data quality and uncertainty, and on machine-readable formats to find, access and use of data; - data structures, data formats, vocabularies, classification schemes, taxonomies and code lists, and how to describe these elements a publicly available and consistent manner; - technical means to access the data, such as application programming interfaces, and their terms of use and quality of service to enable automatic access and transmission of data between parties; - where applicable, the means to enable the interoperability of tools for automating the execution of data sharing contracts. This document is applicable to all organizations participating in dataspaces, regardless of their size or type.
This document specifies requirements and guidance for the interoperability of data, data sharing mechanisms, and services within data spaces. It covers requirements, criteria and implementation guidance on: - dataset content, use restrictions, licences, data collection methodology, data quality and uncertainty, and on machine-readable formats to find, access and use of data; - data structures, data formats, vocabularies, classification schemes, taxonomies and code lists, and how to describe these elements a publicly available and consistent manner; - technical means to access the data, such as application programming interfaces, and their terms of use and quality of service to enable automatic access and transmission of data between parties; - where applicable, the means to enable the interoperability of tools for automating the execution of data sharing contracts. This document is applicable to all organizations participating in dataspaces, regardless of their size or type.
oSIST prEN 18235-3:2026 is classified under the following ICS (International Classification for Standards) categories: 35.030 - IT Security. The ICS classification helps identify the subject area and facilitates finding related standards.
oSIST prEN 18235-3:2026 is associated with the following European legislation: EU Directives/Regulations: 2023/2854; Standardization Mandates: M/614. When a standard is cited in the Official Journal of the European Union, products manufactured in conformity with it benefit from a presumption of conformity with the essential requirements of the corresponding EU directive or regulation.
oSIST prEN 18235-3:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
SLOVENSKI STANDARD
01-julij-2026
Zaupanja vredne podatkovne transakcije - 3. del: Zahteve za interoperabilnost
Trusted data transactions - Part 3: Interoperability requirements
Dataspaces - Interoperailität
Dataspaces - Interopérabilité
Ta slovenski standard je istoveten z: prEN 18235-3
ICS:
35.030 Informacijska varnost IT Security
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
EUROPEAN STANDARD DRAFT
NORME EUROPÉENNE
EUROPÄISCHE NORM
May 2026
ICS 35.030
English version
Trusted data transactions - Part 3: Interoperability
requirements
Dataspaces - Interopérabilité Dataspaces - Interoperailität
This draft European Standard is submitted to CEN members for enquiry. It has been drawn up by the Technical Committee
CEN/CLC/JTC 25.
If this draft becomes a European Standard, CEN and CENELEC members are bound to comply with the CEN/CENELEC Internal
Regulations which stipulate the conditions for giving this European Standard the status of a national standard without any
alteration.
This draft European Standard was established by CEN and CENELEC in three official versions (English, French, German). A
version in any other language made by translation under the responsibility of a CEN and CENELEC member into its own language
and notified to the CEN-CENELEC Management Centre has the same status as the official versions.
CEN and CENELEC members are the national standards bodies and national electrotechnical committees of Austria, Belgium,
Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, France, Germany, Greece, Hungary, Iceland, Ireland, Italy,
Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Republic of North Macedonia, Romania, Serbia,
Slovakia, Slovenia, Spain, Sweden, Switzerland, Türkiye and United Kingdom.
Recipients of this draft are invited to submit, with their comments, notification of any relevant patent rights of which they are
aware and to provide supporting documentation.Recipients of this draft are invited to submit, with their comments, notification
of any relevant patent rights of which they are aware and to provide supporting documentation.
Warning : This document is not a European Standard. It is distributed for review and comments. It is subject to change without
notice and shall not be referred to as a European Standard.
CEN-CENELEC Management Centre:
Rue de la Science 23, B-1040 Brussels
© 2026 CEN/CENELEC All rights of exploitation in any form and by any means
Ref. No. prEN 18235-3:2026 E
reserved worldwide for CEN national Members and for
CENELEC Members.
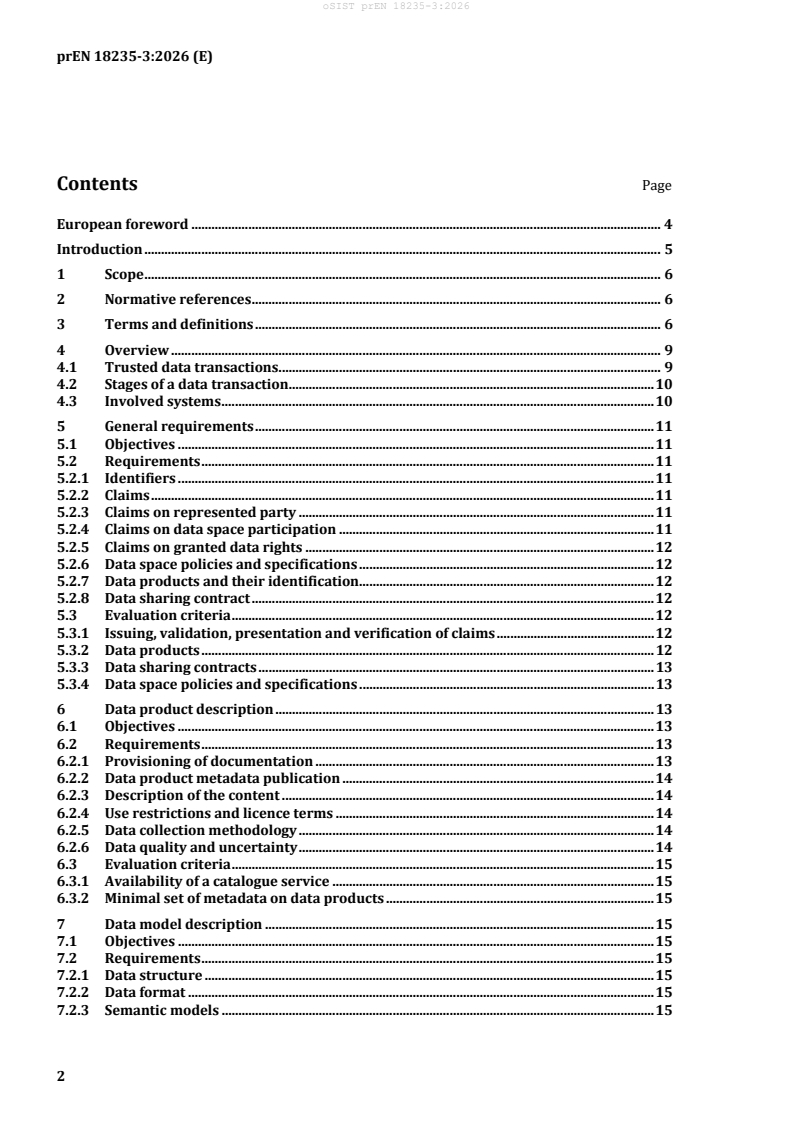
Contents Page
European foreword . 4
Introduction . 5
1 Scope . 6
2 Normative references . 6
3 Terms and definitions . 6
4 Overview . 9
4.1 Trusted data transactions . 9
4.2 Stages of a data transaction . 10
4.3 Involved systems . 10
5 General requirements . 11
5.1 Objectives . 11
5.2 Requirements . 11
5.2.1 Identifiers . 11
5.2.2 Claims . 11
5.2.3 Claims on represented party . 11
5.2.4 Claims on data space participation . 11
5.2.5 Claims on granted data rights . 12
5.2.6 Data space policies and specifications . 12
5.2.7 Data products and their identification . 12
5.2.8 Data sharing contract . 12
5.3 Evaluation criteria . 12
5.3.1 Issuing, validation, presentation and verification of claims . 12
5.3.2 Data products . 12
5.3.3 Data sharing contracts . 13
5.3.4 Data space policies and specifications . 13
6 Data product description . 13
6.1 Objectives . 13
6.2 Requirements . 13
6.2.1 Provisioning of documentation . 13
6.2.2 Data product metadata publication . 14
6.2.3 Description of the content . 14
6.2.4 Use restrictions and licence terms . 14
6.2.5 Data collection methodology . 14
6.2.6 Data quality and uncertainty . 14
6.3 Evaluation criteria . 15
6.3.1 Availability of a catalogue service . 15
6.3.2 Minimal set of metadata on data products . 15
7 Data model description . 15
7.1 Objectives . 15
7.2 Requirements . 15
7.2.1 Data structure . 15
7.2.2 Data format . 15
7.2.3 Semantic models . 15
7.2.4 Classification scheme . 16
7.2.5 Taxonomies . 16
7.2.6 Code lists . 16
7.3 Evaluation criteria. 16
7.3.1 Minimal set of metadata on data representation . 16
8 Data access . 17
8.1 Objectives . 17
8.2 Requirements . 17
8.2.1 Service endpoint for data access . 17
8.2.2 Terms of use of a service endpoint for data access . 17
8.2.3 Nature of the data transmission . 17
8.2.4 Application Programming Interfaces . 17
8.2.5 Service Level Agreement . 17
8.2.6 Required security mechanisms . 18
8.3 Evaluation criteria. 18
8.3.1 Minimal set of metadata on data access . 18
9 Automated negotiation and execution of data sharing contracts . 18
9.1 Objectives . 18
9.2 Requirements . 19
9.2.1 Discovery and negotiation phase . 19
9.2.2 Data Exchange and sharing phase . 19
9.2.3 Observability of the data sharing contract . 20
9.3 Evaluation criteria. 20
9.3.1 Contract negotiation endpoint . 20
9.3.2 Data transfer control endpoint . 20
9.3.3 Observability storage . 20
Annex A (informative) Implementation of interoperability requirements . 21
A.1 General . 21
A.2 Semantics details . 21
Annex ZA (informative) Relationship between this European Standard and the
interoperability requirements of Regulation (EU) 2023/2854 Article 33 aimed to be
covered . 23
Bibliography . 24
European foreword
This document (prEN 18235-3:2026) has been prepared by the Joint Technical Committee CEN-
CENELEC/ JTC 25 “Data Management, Dataspaces, Cloud and Edge”, the secretariat of which is held by
UNI.
This document is currently submitted to the CEN Enquiry.
This document has been prepared under a standardization request addressed to CEN, CENELEC and ETSI
by the European Commission. The Standing Committee of the EFTA States subsequently approves these
requests for its Member States.
For the relationship with EU Legislation, see informative Annex ZA, which is an integral part of this
document.
Introduction
Individuals and organisations increasingly rely on the availability of data shared by others, for doing
research, taking decisions and developing new products and services.
With the advance of technologies for internet of things (IoT), cloud-edge computing and wireless
networking, data can become available at an ever-larger scale. By adopting artificial intelligence (AI)
technologies new opportunities arise for creating value out of this data.
Although all these technologies bring opportunities, they are also add to the complexity of data sharing:
data are no longer residing in individual silos, but are fragmented across the boundaries of different
organisations and systems. Sharing is needed to unlock the potential, while data can be kept at the source.
Individuals and organisations have specific requirements for data protection, for reasons of privacy,
sensitivity and related legal compliance. They want to make informed choices on the data they use and
the data they share with others.
Within a data space, all participants agree to a set of policies, semantic models, protocols and processes,
defined in and managed by a governance framework. Essential requirements are needed to facilitate the
interoperability of data, data sharing mechanisms, services and the data spaces they can operate in.
Increased interoperability can stimulate openness and scale by lower transaction costs in every aspect of
data sharing: finding the right data, negotiating access to data and ensuring that the controlled sharing is
enforced in a proper way. Achieving interoperability of data and data sharing mechanisms is therefore a
critical element for the sustainable growth of the digital economy; leveraging the technological advances
and achieving the desired benefits, while at the same time meeting the need for increased data
sovereignty.
EN 18235-1 Trusted data transactions — Part 1: Terminology, concepts and mechanisms provides the
terminology, concepts and mechanisms for trusted data transactions. prEN 18235-2 Trusted data
transactions — Part 2: Trustworthiness requirements [1] defines the trustworthiness requirements for
trusted data transactions.
The present document, identifies the interoperability requirements for systems used by data space
participants. Annex A describes the implementation of interoperability requirements.
1 Scope
This document specifies requirements and guidance for the interoperability of data, data sharing
mechanisms, and services within data spaces. It covers requirements, criteria and implementation
guidance on:
— dataset content, use restrictions, licences, data collection methodology, data quality and uncertainty,
and on machine-readable formats to find, access and use of data;
— data structures, data formats, vocabularies, classification schemes, taxonomies and code lists, and
how to describe these elements a publicly available and consistent manner;
— technical means to access the data, such as application programming interfaces, and their terms of
use and quality of service to enable automatic access and transmission of data between parties;
— where applicable, the means to enable the interoperability of tools for automating the execution of
data sharing contracts.
This document is applicable to all organizations participating in dataspaces, regardless of their size or
type.
2 Normative references
The following documents are referred to in the text in such a way that some or all of their content
constitutes requirements of this document. For dated references, only the edition cited applies. For
undated references, the latest edition of the referenced document (including any amendments) applies.
EN 18235-1:2026, Trusted data transactions — Part 1: Terminology, concepts and mechanisms
3 Terms and definitions
For the purposes of this document, the terms and definitions given in EN 18235-1:2026 and the following
apply.
ISO and IEC maintain terminology databases for use in standardization at the following addresses:
— ISO Online browsing platform: available at https://www.iso.org/obp/
— IEC Electropedia: available at https://www.electropedia.org/
3.1
identifier
language-independent label, sign or token that uniquely identifies an object within an identification
scheme
[SOURCE: ISO/IEC 19762:2025]
3.2
identification scheme
system for allocating identifiers to registered objects
[SOURCE: ISO/IEC 6523-1:2023]
3.3
uniform resource identifier
URI
compact sequence of characters that identifies an abstract or physical resource
Note 1 to entry: See IETC RFC 3986 (2005).
[SOURCE: ISO/IEC 12785-1:2009]
3.4
semantic model
specification of the meaning of concepts, relationships, and constraints in a given domain, expressed
independently of data structures or data formats
3.5
classification scheme
descriptive information for an arrangement or division of objects into groups based on criteria such as
characteristics, which the objects have in common
EXAMPLE Origin, composition, structure, application, function, etc.
[SOURCE: ISO/IEC 11179-3:2023]
3.6
taxonomy
scheme of categories and subcategories that can be used to sort and otherwise organize itemized
knowledge or information
[SOURCE: ISO 5127:2017, modified: note 1 to entry removed]
3.7
code list
standardized list of code values with a common scope
[SOURCE: ISO/TS 21377:2023]
3.8
agent
active enterprise object that has been delegated something (authorization, responsibility, provision of a
service, etc.) by, and acts for, a party (in exercising the authorization, carrying out the responsibility,
providing the service, etc.)
[SOURCE: ISO/IEC 15414:2015]
3.9
participant agent
agent used to conduct activities in a data space on behalf of a participant
Note 1 to entry: A participant agent is a logical construct and does not necessarily correspond to a single runtime
process
Note 2 to entry: Whilst most interactions take place between participant agents, some interactions with other
systems may be required.
EXAMPLE A participant agent can be implemented by software containing a protocol for exchanging metadata
and a protocol for exchanging claims.
3.10
endpoint
service endpoint
web location where a service can be accessed
3.11
service
logical representation of a set of activities that has specified outcomes, is self-contained, may be
composed of other services, and is a “black box” to consumers of the service
[SOURCE: ISO/IEC 18384-1:2016]
3.12
catalogue service
service that provides access to one or more data catalogues
3.13
discovery service
endpoint of a participant agent to find catalogue services
3.14
data space rulebook
data space governance framework
structured set of principles, processes, standards, protocols, rules and practices that guide and regulate
the governance, management and operations within a data space to ensure effective and responsible
leadership, control, and oversight
Note 1 to entry: ISO/IEC TR 38502:2017 defines governance framework as strategies, policies, decision- making
structures and accountabilities through which the organization’s governance arrangements operate.
[SOURCE: prEN 18235-2]
3.15
claim
statement of something to be true including associated conditions and limitations
Note 1 to entry: The statement of a claim does not mean that the only possible intent or desire is to show it is true.
Sometimes claims are made for the purpose of evaluating whether they are true or false or undertaking an effort to
establish what is true.
Note 2 to entry: In its entirety, a claim conforming to ISO/IEC/IEEE 15026-2 is an unambiguous declaration of an
assertion with any associated conditionality giving explicit details including limitations on values and uncertainty.
It could be about the future, present, or past.
EXAMPLE Attributes of an entity such as its identity, statement of quality, conformity to standards, legal status,
location and so on.
[SOURCE: prEN 18235-2, modified: Note 4 is removed]
3.16
policy
set of rules related to a particular purpose
Note 1 to entry: A rule can be expressed as an obligation, an authorization, a permission or a prohibition.
Note 2 to entry: Policies enable the structured evaluation of claims.
[SOURCE: prEN 18235-2]
3.17
trustworthiness
quality or characteristic of something that is supported by verifiable evidence which can be used to
establish trust
[SOURCE: prEN 18235-2]
3.18
trust framework
set of requirements, rules, roles, responsibilities and assessment mechanisms in support of trust and
trustworthiness
[SOURCE: prEN 18235-2]
4 Overview
4.1 Trusted data transactions
Trusted data transactions pertain to the sharing of data between parties, involving the primary roles of
data provider, data user, and data rights holder, along with other supporting roles as necessary. Data
providers offer data products to data users, who, upon establishing a data sharing contract, gain the right
to access and use these data products.
The concept of a data product is at the core of trusted data transactions, since it bundles all the elements
needed to make data findable, shareable, and usable. Data products combine data, typically in the form
of a dataset, data services, metadata, access and usage policies and can include licensing information. Data
rights holders and data providers rely on data governance processes and supporting systems for the
management of their data products, and data and metadata therein, along the lifecycle of the data product.
Trusted data transactions can happen within the context of a data space. The data space rulebook
provides common rules for participants, which may be generic or domain specific. The data space defines
the applicable trust framework(s), which in turn determine(s) the trust services that are available in the
data space. This allows participants to validate, share, and verify claims between each other on identity,
data space participation, data rights and any other applicable policies.
Agreements between a data provider and data user are recorded in a data sharing contract. During the
sharing or exchange of data, participants ensure that all conditions of the data sharing contract are met.
This is supported by the sharing and verification of claims between participants.
This document defines the requirements for the interoperability of trusted data transactions. The general
requirements for claims, data products and data sharing contracts are covered in Clause 5.2. Detailed
requirements regarding the data product description are covered in Clause 6.2, regarding the data model
description in Clause 7.2, regarding data access in Clause 8.2. Detailed requirements regarding the
automated negotiation, establishment and execution of data sharing contracts are covered in Clause 9.2.
4.2 Stages of a data transaction
During a trusted data transaction, different activities can be identified:
1. Establishing trustworthiness: given the applicable trust frameworks, parties provide evidence to
each other in the form of machine-readable claims. Such claims are presented before and during
trusted transactions with other parties. Claims can be verified using trust services. This results in a
level of trustworthiness.
2. Granting of rights by a data rights holder to a data provider to offer a data product.
3. Data Product Publication, during which activity the data product is published through a catalogue
service.
4. Data Product Discovery, during which a prospective data user queries a catalogue service and
searches for relevant data products. This activity allows the data user to make an assessment
whether the offered data product suits their needs. Discovery services are used to find catalogue
services of data products.
5. Data Sharing Contract Negotiation, during which the data provider and data user agree to the terms
and conditions of the data sharing contract. This can be as simple as agreeing to proposed policies.
More complex negotiation scenarios can be foreseen as well. This activity results in a data sharing
contract.
6. Preparation of the data sharing, relating to activities needed to configure the data access. This
includes the technical set-up of the necessary infrastructure for the sharing of data or use of data
services and the validation of all agreed conditions mentioned in the data sharing contract.
7. Management of the data sharing, relating to the actual start and ending of the sharing of data. Sharing
can take place when the conditions specified in the data sharing contract are met and stop when
these conditions are no longer met. For the purposes of observability and data lineage certain aspects
of the data sharing can be recorded.
Trustworthiness is established at the start of the transaction and is managed during the lifetime of the
data transaction. Participants need to continuously monitor whether any required policies are met. Other
activities occur typically during one of the following phases of a data transaction:
— Granting rights and publication: during this phase typically activities 2 and 3 are performed. It results
in a published data product.
— Discovery and negotiation: during this phase the data provider and data user engage in a process of
discovery of data products and the negotiation of a data sharing contract. This relates to activity 4
and 5. It results in an agreed data sharing contract.
— Data exchange and sharing: During this phase the actual data exchange or sharing takes place,
encompassing the access and usage of the data. The conditions of the data sharing contract are
continuously validated. The phase starts when the contract becomes active and ends when the
contract is terminated.
4.3 Involved systems
Data sharing activities of participants are conducted by participant agents, with most interactions
occurring between these agents. Depending on the set-up within a data space, facilitating services may
be available or sometimes even required to support the process. These services, including trust services,
catalogue services, and discovery services, can play a valuable role in enhancing and streamlining data
sharing activities. This document provides requirements in support of the interoperability of these
systems.
5 General requirements
5.1 Objectives
The objective of this Clause is to provide the general conditions for:
a) setting-up and using participant agents, trust services and other supporting systems and any
required data structures there-in;
b) enabling data users to establish and verify whether the data or data service provided by the data
provider is part of one or more data spaces or not;
c) enabling verification that any required legal and administrative conditions are met.
5.2 Requirements
5.2.1 Identifiers
Entities and objects that are referenced by multiple parties or services shall have a globally unique
identifier.
There are two ways this can be accomplished:
a) using a globally unique scheme to identify the entity or object;
b) using a globally unique scheme to identify the issuing party, in combination with the object or entity
identifier that is unique within the scope of the issuer.
Data space rulebooks may provide further requirements on the syntax and assigning of identifiers.
Identifiers shall meet any further requirements specified in applicable data space rulebooks.
Identifiers based on globally unique schemes shall be in the form of a URI.
5.2.2 Claims
When claims are required, such claims shall be machine readable and verifiable using a trust service
specified in the applicable trust framework.
Claims shall conform to an agreed ontology, defined in the applicable trust framework.
5.2.3 Claims on represented party
In their interactions with participant agents and facilitating services, participant agents shall present a
claim to enable verification of the party on behalf of which it conducts the activities.
5.2.4 Claims on data s
...