

oSIST prEN 304 625 V1.0.0:2026
(Main)Cyber Security (CYBER) - CRA - Cybersecurity requirements for physical and virtual network interfaces
- Abstract
DEN/CYBER-EUS-0017
- Status
- Not Published
- Public Enquiry End Date
- 31-Oct-2026
- Technical Committee
- SPN - Services and Protocols for Networks
- Current Stage
- 4020 - Public enquire (PE) (Adopted Project)
- Start Date
- 10-Aug-2026
- Due Date
- 28-Dec-2026
oSIST prEN 304 625 V1.0.0:2026 is the Slovenian standard identical to ETSI EN 304 625 V1.0.0 (2026-08), published by SIST as a draft harmonised European Standard. It specifies cybersecurity requirements and assessment criteria for physical and virtual network interfaces, so manufacturers, integrators and assessors can judge whether a network interface product with digital elements fits the Cyber Resilience Act (CRA) security model.
What does oSIST prEN 304 625 V1.0.0:2026 specify?
oSIST prEN 304 625 V1.0.0:2026 covers physical and virtual network interfaces in the product context described in clause 4. The standard is aimed at network interfaces that connect a device to a network through a driver API at the data link layer, and it includes wired, wireless and virtual interfaces such as Wi-Fi, Ethernet, Bluetooth, USB, Zigbee, VPN interfaces and similar products.
The scope is narrower than general network equipment. It excludes network interfaces intended for industrial Operational Technology (OT), network interfaces whose purpose includes management or configuration over the attached network, and interfaces whose purpose is routing, switching, or transferring information from one attached network to another.
Clause 4 sets the product context and use cases, clause 5 sets the technical cybersecurity requirements, and clause 6 sets the assessment criteria and compliance verification procedures. Annex A maps the standard to CRA essential requirements, Annex B gives the security analysis used to select applicable requirements, Annex K covers generic cryptographic requirements and assessment, and Annex R adds supplementary requirements when a product relies on Remote Data Processing Solutions (RDPS).
| Annex | What it covers |
|---|---|
| Annex A | Relationship between the standard and CRA essential cybersecurity requirements |
| Annex B | Security analysis, assumptions, threats, risk factors and use-case mapping |
| Annex K | Generic cryptographic requirements and assessment |
| Annex R | Supplementary requirements and assessment for RDPS-dependent product functions |
What are the key requirements of oSIST prEN 304 625 V1.0.0:2026?
oSIST prEN 304 625 V1.0.0:2026 is built around a risk-based set of controls. The most important requirements are in clause 5, and clause 6 repeats each one as an assessment case with objective, preparation, activities, verdict and evidence.
Core product cybersecurity
Appropriate level of cybersecurity - Clause 5.2 and 6.2 require resilience to potentially untrusted inputs. In practice, the product must cope with network traffic and other inputs that may be malformed or hostile, so assessors look for safe handling, not just normal operation.
No known exploitable vulnerabilities - Clause 5.3 and 6.3 require the product to be made available without known exploitable vulnerabilities. For a real project, this means vulnerability review, SBOM/HBOM use where applicable, scan results, and a clear way to justify that identified issues are not exploitable.
Secure by default configuration - Clause 5.4 and 6.4 require methods to protect or disable interfaces, and to protect or disable access to debug or management interfaces. This matters because network interfaces often expose maintenance functions that should not be open in normal use.
Security updates - Clause 5.5 and 6.5 require secure update to be provided by the operational environment. The standard treats update handling as part of the product security story, so the deployer or host environment must be able to keep the interface updated safely.
Authentication, confidentiality and integrity - Clauses 5.6 to 5.8 and 6.6 to 6.8 cover authentication and access control, confidentiality protection, and integrity protection provided by the operational environment. In practice, the document allows some controls to be carried by the host or surrounding system, but the product must fit into a deployment where access, secrecy and tamper protection are handled in a controlled way.
Data minimisation - Clause 5.9 and 6.9 require the product to minimise data processed. That means only data needed for the intended purpose should be handled, which reduces exposure if the interface is attacked or misused.
Availability, monitoring and reset
Availability protection - Clause 5.10 and 6.10 require measures such as fast packet drop, limiting resource usage by incoming network data, availability protection from the operational environment, and watchdog-based notification or self-reset. These are the practical anti-denial-of-service controls, and they matter because a network interface can be overwhelmed before higher-level software sees the attack.
Non-interference - Clause 5.11 and 6.11 require the product to minimise data transmitted to unverified sources. In practice, the interface should not become a vector that harms other products or networks.
Attack surface minimisation - Clause 5.12 and 6.12 require the attack surface to be kept small, including external interfaces. This is especially relevant for products with remote management, host interaction, or multiple exposed services.
Exploit mitigation and monitoring - Clause 5.13 and 5.14, together with 6.13 and 6.14, link exploit mitigation to monitoring and logging, including REQ-MON-01 Logging. The point is to support detection and investigation of suspicious behaviour, not just prevention.
Factory reset and data portability - Clause 5.15 and 6.15 require secure deletion and secure data read provided by the operational environment. For users, this means the product must support a secure return to its default state and handle stored user data in a controlled way.
Annex K and Annex R
Cryptography - Annex K sets generic cryptographic requirements and assessment for product cryptographic configuration, crypto agility, ACM-extended cryptographic mechanisms, and interoperability-based cryptographic mechanisms. If the product uses cryptography, Annex K is where the standard turns that into assessable expectations.
RDPS-dependent products - Annex R applies only when a product relies on Remote Data Processing Solutions for one or more functions. It adds local-side and RDPS-side requirements, threat modelling, and conformity assessment for the product-facing RDPS boundary.
What terms does oSIST prEN 304 625 V1.0.0:2026 define?
oSIST prEN 304 625 V1.0.0:2026 defines the product vocabulary it uses in clause 3 so readers can distinguish the product types and deployment roles.
- Network Interface (NI) - A virtual or physical network interface.
- physical network interface - A hardware device that directly connects to a network through a hardware adapter and a host system communications bus.
- Virtual Network Interface (VNI) - A software-based network interface that simulates a physical network interface.
- device driver - Software or firmware on the host that enables communication on the network via the network interface.
- host - Equipment that gains additional functionality, mainly network connectivity, through the network interface part.
- RDPS - Remote Data Processing Solution, used in Annex R for functions supported across a product-to-remote boundary.
- UC - Use Case, the scenario identifier used to group requirements and risk factors.
- NDDI - Network Device Driver Interface, the standardised interface provided by the host operating system or software framework.
Who uses oSIST prEN 304 625 V1.0.0:2026?
oSIST prEN 304 625 V1.0.0:2026 is used by people who design, integrate, configure, test or assess network interface products with digital elements. The document explicitly names system integrators, internet equipment manufacturers, engineers, professional IT administrators, professional OT administrators, computer repair technicians and moderately skilled computer users as direct users.
It is also relevant to manufacturers of wired, wireless and virtual network interfaces, including products used in home networking, ISPs, mobile devices, smart devices, industrial-connected devices, VPN software, and embedded systems. In practice, buyers and quality managers use it to check whether a supplier’s product fits a CRA-oriented security specification and whether the deployment model relies on the host, the operational environment, or an RDPS boundary.
Which standards are used with oSIST prEN 304 625 V1.0.0:2026?
The standard’s only normative reference is ENISA Report 1747792503, the Agreed Cryptographic Mechanisms (ACM) report. Annex K uses this source when it defines and assesses cryptographic mechanisms.
| Reference | What it contributes |
|---|---|
| ENISA Report 1747792503 (ACM) | Normative source for agreed cryptographic mechanisms used by Annex K |
| prEN 40000-1-1 | Vocabulary for products with digital elements |
| prEN 50770 series | OT security reference used for the OT exclusion in scope |
| ETSI EN 304 627 | Related CRA standard for routers, modems intended for internet connection, and switches |
| ETSI EN 304 636 | Related CRA standard for firewalls, intrusion detection and/or prevention systems |
| RFC 7748, RFC 8032, FIPS 186-5, RFC 9106, RFC 7914, RFC 8439, RFC 7693, RFC 4418, NIST IR 7896, BSI TR-0210 2-1, BSI TR-02102-2/-3/-4 | Cryptographic mechanisms and key-length guidance supporting Annex K |
What does the oSIST prEN 304 625 V1.0.0:2026 document contain?
oSIST prEN 304 625 V1.0.0:2026 contains a product-context clause with architecture descriptions, operational-environment considerations, security-function distribution, user groups, and a set of use cases. It also includes figures for physical and virtual network device architecture and use-case descriptions that help map real products to risk factors.
Clause 5 contains the technical requirement families and the use-case applicability mappings. Clause 6 mirrors those requirements into assessment cases, including objective, preparation, activities, verdict, evidence and guidance, so a conformity assessor can repeat the evaluation in a controlled way.
Annex B contains the risk analysis method, asset list, risk factors, assumptions, threat catalogue, and the mappings from use cases to risk factors and from threats to requirements. Annex A provides the CRA cross-reference, Annex K provides cryptographic assessment structure, and Annex R provides a separate threat model, security requirements and conformity assessment structure for RDPS-dependent functions.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.

DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
oSIST prEN 304 625 V1.0.0:2026 is a standard published by the Slovenian Institute for Standardization (SIST). Its full title is "Cyber Security (CYBER) - CRA - Cybersecurity requirements for physical and virtual network interfaces". This standard covers: DEN/CYBER-EUS-0017
DEN/CYBER-EUS-0017
oSIST prEN 304 625 V1.0.0:2026 is classified under the following ICS (International Classification for Standards) categories: 35.030 - IT Security. The ICS classification helps identify the subject area and facilitates finding related standards.
oSIST prEN 304 625 V1.0.0:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
Draft ETSI EN 304 625 V1.0.0 (2026-08)
HARMONISED EUROPEAN STANDARD
Cyber Security (CYBER); CRA;
Cybersecurity requirements for physical and
virtual network interfaces
2 Draft ETSI EN 304 625 V1.0.0 (2026-08)
Reference
DEN/CYBER-EUS-0017
Keywords
CRA, cybersecurity, interface
ETSI
650 Route des Lucioles
F-06921 Sophia Antipolis Cedex - FRANCE
Tel.: +33 4 92 94 42 00 Fax: +33 4 93 65 47 16
Siret N° 348 623 562 00017 - APE 7112B
Association à but non lucratif enregistrée à la
Sous-Préfecture de Grasse (06) N° w061004871
Important notice
The present document can be downloaded from the
ETSI Search & Browse Standards application.
The present document may be made available in electronic versions and/or in print. The content of any electronic and/or
print versions of the present document shall not be modified without the prior written authorization of ETSI. In case of any
existing or perceived difference in contents between such versions and/or in print, the prevailing version of an ETSI
deliverable is the one made publicly available in PDF format on ETSI deliver repository.
Users should be aware that the present document may be revised or have its status changed,
this information is available in the Milestones listing.
If you find errors in the present document, please send your comments to
the relevant service listed under Committee Support Staff.
If you find a security vulnerability in the present document, please report it through our
Coordinated Vulnerability Disclosure (CVD) program.
Notice of disclaimer & limitation of liability
The information provided in the present deliverable is directed solely to professionals who have the appropriate degree of
experience to understand and interpret its content in accordance with generally accepted engineering or
other professional standard and applicable regulations.
No recommendation as to products and services or vendors is made or should be implied.
In no event shall ETSI be held liable for loss of profits or any other incidental or consequential damages.
Any software contained in this deliverable is provided "AS IS" with no warranties, express or implied, including but not
limited to, the warranties of merchantability, fitness for a particular purpose and non-infringement of intellectual property
rights and ETSI shall not be held liable in any event for any damages whatsoever (including, without limitation, damages
for loss of profits, business interruption, loss of information; or any other pecuniary loss) arising out of or related to the use
of or inability to use the software.
Copyright Notification
No part of this document may be reproduced in any form, by any means and in any media, without the prior written
authorization of ETSI and except as expressly permitted below.
By way of exception and when the document is a normative deliverable (European Standard (EN),
Technical Specification (TS), Group Specification (GS) or ETSI Standard (ES)), ETSI authorizes to reproduce
and incorporate into products, services and technical documentation only those extracts (e.g. templates) that are strictly
necessary for the technical implementation of the normative deliverable, to ensure compliance with the latter.
Nothing in this notice shall be construed as limiting any mandatory exceptions to copyright provided by applicable law.
© ETSI 2026.
All rights reserved.
ETSI
3 Draft ETSI EN 304 625 V1.0.0 (2026-08)
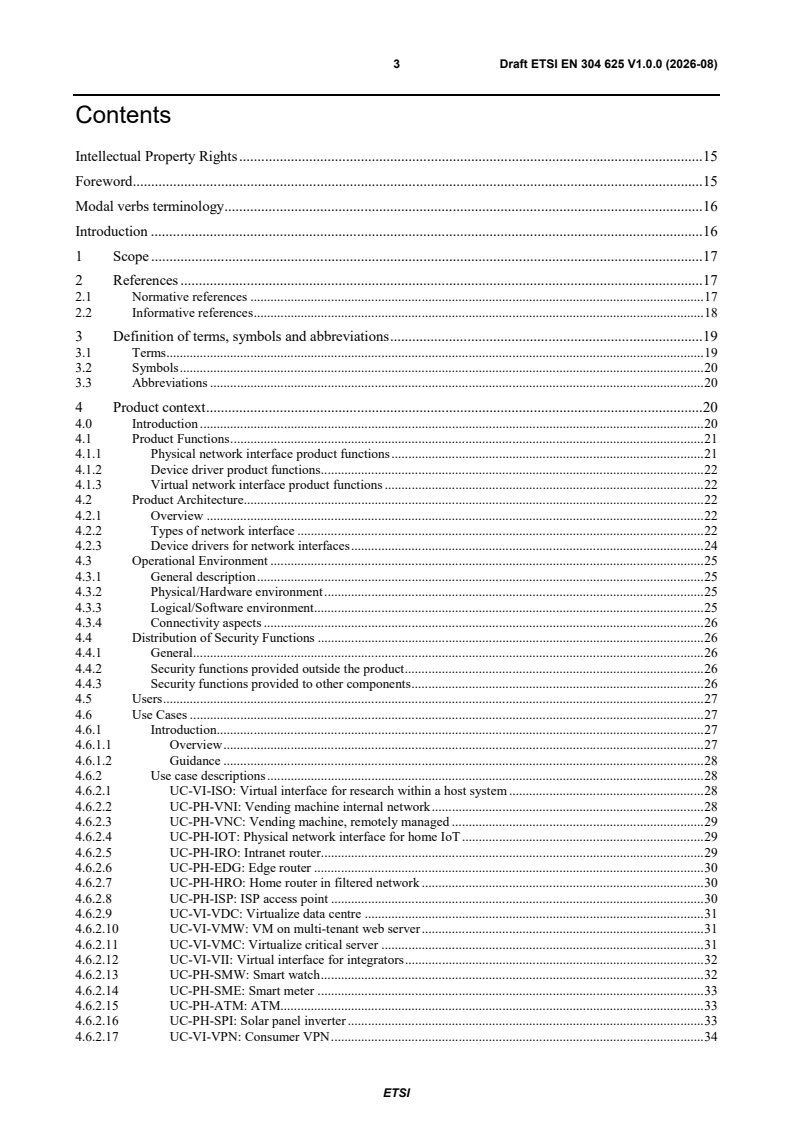
Contents
Intellectual Property Rights . 15
Foreword . 15
Modal verbs terminology . 16
Introduction . 16
1 Scope . 17
2 References . 17
2.1 Normative references . 17
2.2 Informative references . 18
3 Definition of terms, symbols and abbreviations . 19
3.1 Terms . 19
3.2 Symbols . 20
3.3 Abbreviations . 20
4 Product context . 20
4.0 Introduction . 20
4.1 Product Functions . 21
4.1.1 Physical network interface product functions . 21
4.1.2 Device driver product functions . 22
4.1.3 Virtual network interface product functions . 22
4.2 Product Architecture. 22
4.2.1 Overview . 22
4.2.2 Types of network interface . 22
4.2.3 Device drivers for network interfaces . 24
4.3 Operational Environment . 25
4.3.1 General description . 25
4.3.2 Physical/Hardware environment . 25
4.3.3 Logical/Software environment. 25
4.3.4 Connectivity aspects . 26
4.4 Distribution of Security Functions . 26
4.4.1 General . 26
4.4.2 Security functions provided outside the product . 26
4.4.3 Security functions provided to other components . 26
4.5 Users . 27
4.6 Use Cases . 27
4.6.1 Introduction. 27
4.6.1.1 Overview . 27
4.6.1.2 Guidance . 28
4.6.2 Use case descriptions . 28
4.6.2.1 UC-VI-ISO: Virtual interface for research within a host system . 28
4.6.2.2 UC-PH-VNI: Vending machine internal network . 28
4.6.2.3 UC-PH-VNC: Vending machine, remotely managed . 29
4.6.2.4 UC-PH-IOT: Physical network interface for home IoT . 29
4.6.2.5 UC-PH-IRO: Intranet router. 29
4.6.2.6 UC-PH-EDG: Edge router . 30
4.6.2.7 UC-PH-HRO: Home router in filtered network . 30
4.6.2.8 UC-PH-ISP: ISP access point . 30
4.6.2.9 UC-VI-VDC: Virtualize data centre . 31
4.6.2.10 UC-VI-VMW: VM on multi-tenant web server . 31
4.6.2.11 UC-VI-VMC: Virtualize critical server . 31
4.6.2.12 UC-VI-VII: Virtual interface for integrators . 32
4.6.2.13 UC-PH-SMW: Smart watch . 32
4.6.2.14 UC-PH-SME: Smart meter . 33
4.6.2.15 UC-PH-ATM: ATM. 33
4.6.2.16 UC-PH-SPI: Solar panel inverter . 33
4.6.2.17 UC-VI-VPN: Consumer VPN . 34
ETSI
4 Draft ETSI EN 304 625 V1.0.0 (2026-08)
4.6.2.18 UC-PH-MOB: Mobile phone or tablet . 34
4.6.2.19 UC-PH-GPI: General purpose integrated . 34
4.6.2.20 UC-PH-USB: External USB . 35
4.6.2.21 UC-PH-STA: Standalone . 35
4.6.2.22 UC-PH-SNS: Remote Sensor . 35
5 Technical requirements for products . 36
5.1 Introduction . 36
5.1.1 Applicability of the requirements . 36
5.1.2 Applicability of Annex K . 36
5.1.3 Applicability of Annex R . 36
5.1.4 Guidance for "cybersecurity-relevant" . 36
5.2 Appropriate level of cybersecurity . 37
5.2.1 Overview . 37
5.2.1.1 CRA Relevance . 37
5.2.2 REQ-ALC-01 Resilience to potentially untrusted inputs . 37
5.2.2.1 Requirement . 37
5.2.2.2 Applicability. 37
5.2.3 Mapping of requirements to use cases . 38
5.3 No known exploitable vulnerabilities . 38
5.3.1 Overview . 38
5.3.2 REQ-KEV-01 No known exploitable vulnerabilities . 38
5.3.2.1 Requirement . 38
5.3.2.2 Applicability. 38
5.3.2.3 Guidance . 39
5.3.3 Mapping of requirements to use cases . 40
5.4 Secure by default configuration . 40
5.4.1 Overview . 40
5.4.2 REQ-SBD-01: Provide methods to protect or disable interfaces . 40
5.4.2.1 Requirement . 40
5.4.2.2 Applicability. 40
5.4.2.3 Guidance . 41
5.4.3 REQ-SBD-02: Protect or disable access to debug or management interfaces . 41
5.4.3.1 Requirement . 41
5.4.3.2 Applicability. 41
5.4.3.3 Guidance . 42
5.4.4 Mapping of requirements to use cases . 42
5.5 Security updates . 42
5.5.1 Overview . 42
5.5.2 REQ-SU-01: Secure update provided by operational environment . 43
5.5.2.1 Requirement . 43
5.5.2.2 Applicability. 43
5.5.3 Mapping of requirements to use cases . 44
5.6 Authentication and access control . 44
5.6.1 Overview . 44
5.6.2 REQ-AAC-01: Authentication and access control provided by operational environment. 44
5.6.2.1 Requirement . 44
5.6.2.2 Applicability. 44
5.6.3 Mapping of requirements to use cases . 45
5.7 Confidentiality protection . 46
5.7.1 Overview . 46
5.7.2 REQ-CP-01: Confidentiality protection provided by operational environment . 46
5.7.2.1 Requirement . 46
5.7.2.2 Applicability. 46
5.7.2.3 Guidance . 47
5.7.3 Mapping of requirements to use cases . 47
5.8 Integrity protection . 47
5.8.1 Overview . 47
5.8.2 REQ-IP-01: Integrity protection provided by operational environment . 47
5.8.2.1 Requirement . 47
5.8.2.2 Applicability. 47
5.8.3 Mapping of requirements to use cases . 48
ETSI
5 Draft ETSI EN 304 625 V1.0.0 (2026-08)
5.9 Data minimisation . 49
5.9.1 Overview . 49
5.9.2 REQ-DM-01: Data minimisation . 49
5.9.2.1 Requirement . 49
5.9.2.2 Applicability. 49
5.9.3 Mapping of requirements to use cases . 50
5.10 Availability protection . 50
5.10.1 Overview . 50
5.10.2 REQ-AP-01 Fast packet drop . 50
5.10.2.1 Requirement . 50
5.10.2.2 Applicability. 50
5.10.2.3 Guidance . 51
5.10.3 REQ-AP-02 Limit resource usage by incoming network data . 51
5.10.3.1 Requirement . 51
5.10.3.2 Applicability. 51
5.10.4 REQ-AP-03 Availability protection provided by operational environment . 52
5.10.4.1 Requirement . 52
5.10.4.2 Applicability. 52
5.10.5 REQ-AP-04: Watchdog and notification of host . 53
5.10.5.1 Requirement . 53
5.10.5.2 Applicability. 53
5.10.6 REQ-AP-05: Watchdog and self-initiated reset . 54
5.10.6.1 Requirement . 54
5.10.6.2 Applicability. 54
5.10.7 Mapping of requirements to use cases . 55
5.11 Non-interference . 55
5.11.1 Overview . 55
5.11.2 REQ-NI-01: Minimise data transmitted to unverified sources . 55
5.11.2.1 Requirement . 55
5.11.2.2 Applicability. 55
5.11.2.3 Guidance . 56
5.11.3 Mapping of requirements to use cases . 57
5.12 Attack surface minimisation . 57
5.12.1 Overview . 57
5.12.2 REQ-ASM-01: Minimise attack surface . 57
5.12.2.1 Requirement . 57
5.12.2.2 Applicability. 57
5.12.3 Mapping of requirements to use cases . 58
5.13 Exploit mitigation . 58
5.13.1 Overview . 58
5.13.2 Requirements . 58
5.13.3 Mapping of requirements to use cases . 59
5.14 Monitoring . 59
5.14.1 Overview . 59
5.14.2 REQ-MON-01: Logging . 59
5.14.2.1 Requirement . 59
5.14.2.2 Applicability. 59
5.14.3 Mapping of requirements to use cases . 60
5.15 Factory reset and data portability . 60
5.15.1 Overview . 60
5.15.2 REQ-SDT-01 Secure deletion. 61
5.15.2.1 Requirement . 61
5.15.2.2 Applicability. 61
5.15.3 REQ-SDT-02 Secure data read provided by operational environment . 62
5.15.3.1 Requirement . 62
5.15.3.2 Applicability. 62
5.15.4 Mapping of requirements to use cases . 63
6 Assessment criteria for compliance with technical requirements . 63
6.1 Introduction to the assessment and compliance criteria . 63
6.1.1 General . 63
6.1.2 Guidance for identifying interfaces or data processing . 65
ETSI
6 Draft ETSI EN 304 625 V1.0.0 (2026-08)
6.2 Appropriate level of cybersecurity . 65
6.2.1 Overview . 65
6.2.2 REQ-ALC-01 Resilience to potentially untrusted inputs . 65
6.2.2.1 Objective . 65
6.2.2.2 Preparation . 66
6.2.2.3 Activities . 67
6.2.2.4 Verdict . 67
6.2.2.5 Evidence . 67
6.2.2.6 Guidance . 67
6.3 No known exploitable vulnerabilities . 68
6.3.1 Overview . 68
6.3.2 REQ-KEV-01 No known exploitable vulnerabilities . 68
6.3.2.1 Objective . 68
6.3.2.2 Preparation . 68
6.3.2.3 Activities . 68
6.3.2.4 Verdict . 68
6.3.2.5 Evidence . 68
6.3.2.6 Guidance . 69
6.4 Secure by default configuration . 69
6.4.1 Overview . 69
6.4.2 REQ-SBD-01: Provide methods to protect or disable interfaces . 69
6.4.2.1 Objective . 69
6.4.2.2 Preparation . 69
6.4.2.3 Activities . 69
6.4.2.4 Verdict . 69
6.4.2.5 Evidence . 70
6.4.2.6 Guidance . 70
6.4.3 REQ-SBD-02: Protect or disable access to debug or management interfaces . 70
6.4.3.1 Objective . 70
6.4.3.2 Preparation . 70
6.4.3.3 Activities . 70
6.4.3.4 Verdict . 70
6.4.3.5 Evidence . 71
6.5 Security updates . 71
6.5.1 Overview . 71
6.5.2 REQ-SU-01 Secure update provided by operational environment . 71
6.5.2.1 Objective . 71
6.5.2.2 Preparation . 71
6.5.2.3 Activities . 71
6.5.2.4 Verdict . 71
6.5.2.5 Evidence . 71
6.5.2.6 Guidance . 72
6.6 Authentication and access control . 72
6.6.1 Overview . 72
6.6.2 REQ-AAC-01: Authentication and access control provided by operational environment. 72
6.6.2.1 Objective . 72
6.6.2.2 Preparation . 72
6.6.2.3 Activities . 72
6.6.2.4 Verdict . 72
6.6.2.5 Evidence . 72
6.7 Confidentiality protection . 72
6.7.1 Overview . 72
6.7.2 REQ-CP-01: Confidentiality protection provided by operational environment . 73
6.7.2.1 Objective . 73
6.7.2.2 Preparation . 73
6.7.2.3 Activities . 73
6.7.2.4 Verdict . 73
6.7.2.5 Evidence . 73
6.7.2.6 Guidance . 73
6.8 Integrity protection . 74
6.8.1 Overview . 74
6.8.2 REQ-IP-01: Integrity protection provided by operational environment . 74
ETSI
7 Draft ETSI EN 304 625 V1.0.0 (2026-08)
6.8.2.1 Objective . 74
6.8.2.2 Preparation . 74
6.8.2.3 Activities . 74
6.8.2.4 Verdict . 74
6.8.2.5 Evidence . 74
6.8.2.6 Guidance . 74
6.9 Data minimisation . 75
6.9.1 Overview . 75
6.9.2 REQ-DM-01: Minimise data processed . 75
6.9.2.1 Objective . 75
6.9.2.2 Preparation . 75
6.9.2.3 Activities . 75
6.9.2.4 Verdict . 75
6.9.2.5 Evidence . 75
6.9.2.6 Guidance . 76
6.10 Availability protection . 76
6.10.1 Overview . 76
6.10.2 REQ-AP-01 Fast packet drop . 76
6.10.2.1 Objective . 76
6.10.2.2 Preparation .
...
SLOVENSKI STANDARD
01-oktober-2026
Kibernetska varnost (CYBER) - CRA - Zahteve za kibernetsko varnost za fizične in
virtualne omrežne vmesnike
Cyber Security (CYBER) - CRA - Cybersecurity requirements for physical and virtual
network interfaces
Ta slovenski standard je istoveten z: ETSI EN 304 625 V1.0.0 (2026-08)
ICS:
35.030 Informacijska varnost IT Security
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
Draft ETSI EN 304 625 V1.0.0 (2026-08)
HARMONISED EUROPEAN STANDARD
Cyber Security (CYBER); CRA;
Cybersecurity requirements for physical and
virtual network interfaces
2 Draft ETSI EN 304 625 V1.0.0 (2026-08)
Reference
DEN/CYBER-EUS-0017
Keywords
CRA, cybersecurity, interface
ETSI
650 Route des Lucioles
F-06921 Sophia Antipolis Cedex - FRANCE
Tel.: +33 4 92 94 42 00 Fax: +33 4 93 65 47 16
Siret N° 348 623 562 00017 - APE 7112B
Association à but non lucratif enregistrée à la
Sous-Préfecture de Grasse (06) N° w061004871
Important notice
The present document can be downloaded from the
ETSI Search & Browse Standards application.
The present document may be made available in electronic versions and/or in print. The content of any electronic and/or
print versions of the present document shall not be modified without the prior written authorization of ETSI. In case of any
existing or perceived difference in contents between such versions and/or in print, the prevailing version of an ETSI
deliverable is the one made publicly available in PDF format on ETSI deliver repository.
Users should be aware that the present document may be revised or have its status changed,
this information is available in the Milestones listing.
If you find errors in the present document, please send your comments to
the relevant service listed under Committee Support Staff.
If you find a security vulnerability in the present document, please report it through our
Coordinated Vulnerability Disclosure (CVD) program.
Notice of disclaimer & limitation of liability
The information provided in the present deliverable is directed solely to professionals who have the appropriate degree of
experience to understand and interpret its content in accordance with generally accepted engineering or
other professional standard and applicable regulations.
No recommendation as to products and services or vendors is made or should be implied.
In no event shall ETSI be held liable for loss of profits or any other incidental or consequential damages.
Any software contained in this deliverable is provided "AS IS" with no warranties, express or implied, including but not
limited to, the warranties of merchantability, fitness for a particular purpose and non-infringement of intellectual property
rights and ETSI shall not be held liable in any event for any damages whatsoever (including, without limitation, damages
for loss of profits, business interruption, loss of information; or any other pecuniary loss) arising out of or related to the use
of or inability to use the software.
Copyright Notification
No part of this document may be reproduced in any form, by any means and in any media, without the prior written
authorization of ETSI and except as expressly permitted below.
By way of exception and when the document is a normative deliverable (European Standard (EN),
Technical Specification (TS), Group Specification (GS) or ETSI Standard (ES)), ETSI authorizes to reproduce
and incorporate into products, services and technical documentation only those extracts (e.g. templates) that are strictly
necessary for the technical implementation of the normative deliverable, to ensure compliance with the latter.
Nothing in this notice shall be construed as limiting any mandatory exceptions to copyright provided by applicable law.
© ETSI 2026.
All rights reserved.
ETSI
3 Draft ETSI EN 304 625 V1.0.0 (2026-08)
Contents
Intellectual Property Rights . 15
Foreword . 15
Modal verbs terminology . 16
Introduction . 16
1 Scope . 17
2 References . 17
2.1 Normative references . 17
2.2 Informative references . 18
3 Definition of terms, symbols and abbreviations . 19
3.1 Terms . 19
3.2 Symbols . 20
3.3 Abbreviations . 20
4 Product context . 20
4.0 Introduction . 20
4.1 Product Functions . 21
4.1.1 Physical network interface product functions . 21
4.1.2 Device driver product functions . 22
4.1.3 Virtual network interface product functions . 22
4.2 Product Architecture. 22
4.2.1 Overview . 22
4.2.2 Types of network interface . 22
4.2.3 Device drivers for network interfaces . 24
4.3 Operational Environment . 25
4.3.1 General description . 25
4.3.2 Physical/Hardware environment . 25
4.3.3 Logical/Software environment. 25
4.3.4 Connectivity aspects . 26
4.4 Distribution of Security Functions . 26
4.4.1 General . 26
4.4.2 Security functions provided outside the product . 26
4.4.3 Security functions provided to other components . 26
4.5 Users . 27
4.6 Use Cases . 27
4.6.1 Introduction. 27
4.6.1.1 Overview . 27
4.6.1.2 Guidance . 28
4.6.2 Use case descriptions . 28
4.6.2.1 UC-VI-ISO: Virtual interface for research within a host system . 28
4.6.2.2 UC-PH-VNI: Vending machine internal network . 28
4.6.2.3 UC-PH-VNC: Vending machine, remotely managed . 29
4.6.2.4 UC-PH-IOT: Physical network interface for home IoT . 29
4.6.2.5 UC-PH-IRO: Intranet router. 29
4.6.2.6 UC-PH-EDG: Edge router . 30
4.6.2.7 UC-PH-HRO: Home router in filtered network . 30
4.6.2.8 UC-PH-ISP: ISP access point . 30
4.6.2.9 UC-VI-VDC: Virtualize data centre . 31
4.6.2.10 UC-VI-VMW: VM on multi-tenant web server . 31
4.6.2.11 UC-VI-VMC: Virtualize critical server . 31
4.6.2.12 UC-VI-VII: Virtual interface for integrators . 32
4.6.2.13 UC-PH-SMW: Smart watch . 32
4.6.2.14 UC-PH-SME: Smart meter . 33
4.6.2.15 UC-PH-ATM: ATM. 33
4.6.2.16 UC-PH-SPI: Solar panel inverter . 33
4.6.2.17 UC-VI-VPN: Consumer VPN . 34
ETSI
4 Draft ETSI EN 304 625 V1.0.0 (2026-08)
4.6.2.18 UC-PH-MOB: Mobile phone or tablet . 34
4.6.2.19 UC-PH-GPI: General purpose integrated . 34
4.6.2.20 UC-PH-USB: External USB . 35
4.6.2.21 UC-PH-STA: Standalone . 35
4.6.2.22 UC-PH-SNS: Remote Sensor . 35
5 Technical requirements for products . 36
5.1 Introduction . 36
5.1.1 Applicability of the requirements . 36
5.1.2 Applicability of Annex K . 36
5.1.3 Applicability of Annex R . 36
5.1.4 Guidance for "cybersecurity-relevant" . 36
5.2 Appropriate level of cybersecurity . 37
5.2.1 Overview . 37
5.2.1.1 CRA Relevance . 37
5.2.2 REQ-ALC-01 Resilience to potentially untrusted inputs . 37
5.2.2.1 Requirement . 37
5.2.2.2 Applicability. 37
5.2.3 Mapping of requirements to use cases . 38
5.3 No known exploitable vulnerabilities . 38
5.3.1 Overview . 38
5.3.2 REQ-KEV-01 No known exploitable vulnerabilities . 38
5.3.2.1 Requirement . 38
5.3.2.2 Applicability. 38
5.3.2.3 Guidance . 39
5.3.3 Mapping of requirements to use cases . 40
5.4 Secure by default configuration . 40
5.4.1 Overview . 40
5.4.2 REQ-SBD-01: Provide methods to protect or disable interfaces . 40
5.4.2.1 Requirement . 40
5.4.2.2 Applicability. 40
5.4.2.3 Guidance . 41
5.4.3 REQ-SBD-02: Protect or disable access to debug or management interfaces . 41
5.4.3.1 Requirement . 41
5.4.3.2 Applicability. 41
5.4.3.3 Guidance . 42
5.4.4 Mapping of requirements to use cases . 42
5.5 Security updates . 42
5.5.1 Overview . 42
5.5.2 REQ-SU-01: Secure update provided by operational environment . 43
5.5.2.1 Requirement . 43
5.5.2.2 Applicability. 43
5.5.3 Mapping of requirements to use cases . 44
5.6 Authentication and access control . 44
5.6.1 Overview . 44
5.6.2 REQ-AAC-01: Authentication and access control provided by operational environment. 44
5.6.2.1 Requirement . 44
5.6.2.2 Applicability. 44
5.6.3 Mapping of requirements to use cases . 45
5.7 Confidentiality protection . 46
5.7.1 Overview . 46
5.7.2 REQ-CP-01: Confidentiality protection provided by operational environment . 46
5.7.2.1 Requirement . 46
5.7.2.2 Applicability. 46
5.7.2.3 Guidance . 47
5.7.3 Mapping of requirements to use cases . 47
5.8 Integrity protection . 47
5.8.1 Overview . 47
5.8.2 REQ-IP-01: Integrity protection provided by operational environment . 47
5.8.2.1 Requirement . 47
5.8.2.2 Applicability. 47
5.8.3 Mapping of requirements to use cases . 48
ETSI
5 Draft ETSI EN 304 625 V1.0.0 (2026-08)
5.9 Data minimisation . 49
5.9.1 Overview . 49
5.9.2 REQ-DM-01: Data minimisation . 49
5.9.2.1 Requirement . 49
5.9.2.2 Applicability. 49
5.9.3 Mapping of requirements to use cases . 50
5.10 Availability protection . 50
5.10.1 Overview . 50
5.10.2 REQ-AP-01 Fast packet drop . 50
5.10.2.1 Requirement . 50
5.10.2.2 Applicability. 50
5.10.2.3 Guidance . 51
5.10.3 REQ-AP-02 Limit resource usage by incoming network data . 51
5.10.3.1 Requirement . 51
5.10.3.2 Applicability. 51
5.10.4 REQ-AP-03 Availability protection provided by operational environment . 52
5.10.4.1 Requirement . 52
5.10.4.2 Applicability. 52
5.10.5 REQ-AP-04: Watchdog and notification of host . 53
5.10.5.1 Requirement . 53
5.10.5.2 Applicability. 53
5.10.6 REQ-AP-05: Watchdog and self-initiated reset . 54
5.10.6.1 Requirement . 54
5.10.6.2 Applicability. 54
5.10.7 Mapping of requirements to use cases . 55
5.11 Non-interference . 55
5.11.1 Overview . 55
5.11.2 REQ-NI-01: Minimise data transmitted to unverified sources . 55
5.11.2.1 Requirement . 55
5.11.2.2 Applicability. 55
5.11.2.3 Guidance . 56
5.11.3 Mapping of requirements to use cases . 57
5.12 Attack surface minimisation . 57
5.12.1 Overview . 57
5.12.2 REQ-ASM-01: Minimise attack surface . 57
5.12.2.1 Requirement . 57
5.12.2.2 Applicability. 57
5.12.3 Mapping of requirements to use cases . 58
5.13 Exploit mitigation . 58
5.13.1 Overview . 58
5.13.2 Requirements . 58
5.13.3 Mapping of requirements to use cases . 59
5.14 Monitoring . 59
5.14.1 Overview . 59
5.14.2 REQ-MON-01: Logging . 59
5.14.2.1 Requirement . 59
5.14.2.2 Applicability. 59
5.14.3 Mapping of requirements to use cases . 60
5.15 Factory reset and data portability . 60
5.15.1 Overview . 60
5.15.2 REQ-SDT-01 Secure deletion. 61
5.15.2.1 Requirement . 61
5.15.2.2 Applicability. 61
5.15.3 REQ-SDT-02 Secure data read provided by operational environment . 62
5.15.3.1 Requirement . 62
5.15.3.2 Applicability. 62
5.15.4 Mapping of requirements to use cases . 63
6 Assessment criteria for compliance with technical requirements . 63
6.1 Introduction to the assessment and compliance criteria . 63
6.1.1 General . 63
6.1.2 Guidance for identifying interfaces or data processing . 65
ETSI
6 Draft ETSI EN 304 625 V1.0.0 (2026-08)
6.2 Appropriate level of cybersecurity . 65
6.2.1 Overview . 65
6.2.2 REQ-ALC-01 Resilience to potentially untrusted inputs . 65
6.2.2.1 Objective . 65
6.2.2.2 Preparation . 66
6.2.2.3 Activities . 67
6.2.2.4 Verdict . 67
6.2.2.5 Evidence . 67
6.2.2.6 Guidance . 67
6.3 No known exploitable vulnerabilities . 68
6.3.1 Overview . 68
6.3.2 REQ-KEV-01 No known exploitable vulnerabilities . 68
6.3.2.1 Objective . 68
6.3.2.2 Preparation . 68
6.3.2.3 Activities . 68
6.3.2.4 Verdict . 68
6.3.2.5 Evidence . 68
6.3.2.6 Guidance . 69
6.4 Secure by default configuration . 69
6.4.1 Overview . 69
6.4.2 REQ-SBD-01: Provide methods to protect or disable interfaces . 69
6.4.2.1 Objective . 69
6.4.2.2 Preparation . 69
6.4.2.3 Activities . 69
6.4.2.4 Verdict . 69
6.4.2.5 Evidence . 70
6.4.2.6 Guidance . 70
6.4.3 REQ-SBD-02: Protect or disable access to debug or management interfaces . 70
6.4.3.1 Objective . 70
6.4.3.2 Preparation . 70
6.4.3.3 Activities . 70
6.4.3.4 Verdict . 70
6.4.3.5 Evidence . 71
6.5 Security updates . 71
6.5.1 Overview . 71
6.5.2 REQ-SU-01 Secure update provided by operational environment . 71
6.5.2.1 Objective . 71
6.5.2.2 Preparation . 71
6.5.2.3 Activities . 71
6.5.2.4 Verdict . 71
6.5.2.5 Evidence . 71
6.5.2.6 Guidance . 72
6.6 Authentication and access control . 72
6.6.1 Overview . 72
6.6.2 REQ-AAC-01: Authentication and access control provided by operational environment. 72
6.6.2.1 Objective . 72
6.6.2.2 Preparation . 72
6.6.2.3 Activities . 72
6.6.2.4 Verdict . 72
6.6.2.5 Evidence . 72
6.7 Confidentiality protection . 72
6.7.1 Overview . 72
6.7.2 REQ-CP-01: Confidentiality protection provided by operational environment . 73
6.7.2.1 Objective . 73
6.7.2.2 Preparation . 73
6.7.2.3 Activities . 73
6.7.2.4 Verdict . 73
6.7.2.5 Evidence . 73
6.7.2.6 Guidance . 73
6.8 Integrity protection . 74
6.8.1 Overview . 74
6.8.2 REQ-IP-01: Integrity protection provided by operational environment . 74
ETSI
7 Draft ETSI EN 304 625 V1.0.0 (2026-08)
6.8.2.1 Objective . 74
6.8.2.2 Preparation . 74
6.8.2.3 Activities . 74
6.8.2.4 Verdict . 74
6.8.2.5 Evidence . 74
6.8.2.6 Guidance . 74
6.9 Data minimisation . 75
6.9.1 Overview . 75
6.9.2 REQ-DM-01: Minimise data processed . 75
6.9.2.1 Objective . 75
6.9.2.2 Preparation . 75
6.9.2.3 Activities . 75
6.9.2.4 Verdict . 75
6.9.2.5 Evidence .
...