

oSIST prEN 304 624 V1.0.0:2026
(Main)Cyber Security (CYBER) - CRA - Cybersecurity requirements for Public key infrastructure and digital certificate issuance software
- Abstract
DEN/CYBER-EUS-0015
- Status
- Not Published
- Public Enquiry End Date
- 28-Oct-2026
- Technical Committee
- SPN - Services and Protocols for Networks
- Current Stage
- 4020 - Public enquire (PE) (Adopted Project)
- Start Date
- 10-Aug-2026
- Due Date
- 28-Dec-2026
oSIST prEN 304 624 V1.0.0:2026 is the Slovenian draft standard published by SIST and identical to ETSI EN 304 624 V1.0.0 (2026-08). It specifies technical cybersecurity requirements and assessment criteria for public key infrastructure (PKI) and digital certificate issuance software. The standard is meant for product developers, operators, assessors, and buyers who need to judge whether a PKI product can manage certificates and associated keys in a CRA-oriented way.
What does oSIST prEN 304 624 V1.0.0:2026 specify?
oSIST prEN 304 624 V1.0.0:2026 applies to products with digital elements used in PKI that manage certificate and key lifecycles, including validation, creation, issuance, distribution, status publication, renewal, and revocation of digital certificates. It also covers the generation, storage, escrow, exchange, destruction, and rotation of cryptographic keys associated with those certificates.
The document uses use cases to scope the requirements rather than trying to cover every PKI deployment. Clause 4 describes the product context, clause 5 sets the technical cybersecurity requirements, and clause 6 gives the assessment criteria used to check compliance.
| Annex | What it covers |
|---|---|
| Annex A | Relationship between the standard and the Cyber Resilience Act |
| Annex B | Security analysis and risk assessment method |
| Annex K | Generic cryptographic requirements and assessment |
| Annex U | Detailed use-case context, functions, assets, environment, security function distribution, and users |
| Annexes C to J | Void |
What are the key requirements of oSIST prEN 304 624 V1.0.0:2026?
oSIST prEN 304 624 V1.0.0:2026 combines product-security requirements with assessment criteria. The most important points are the handling of vulnerabilities, updates, access control, cryptography, certificate trust, logging, and data protection.
Clause 5.2 - No known exploitable vulnerabilities. The product shall not contain known exploitable vulnerabilities unless assessment shows that the vulnerability is not exploitable in the product or that user guidance prevents exploitation. In practice, a supplier needs vulnerability tracking and evidence for each identified issue.
Clause 5.4 - Secure updates. The product shall support updating all mutable software parts, and updates shall only be installed when signed by a known and trusted entity with a valid PKC. The product administrator shall also be able to control when updates are installed. This matters because certificate platforms need patching without accepting tampered code.
Clause 5.5 - Authentication and access control. Only authorised users shall access product functions, stored data, and configuration data, and the product shall use identification and authentication based on cryptographic mechanisms conforming to Annex K. The clause also requires RBAC for privileged roles. That means administrators, officers, and auditors need separated rights, not shared access.
Clause 5.6 - Confidentiality. The product shall protect confidentiality for stored and transmitted data, including key material, and pseudonymous certificates shall not contain data that can break sender pseudonymity. The requirements also cover secure storage and communications, plus key management. In practice, secret keys must not be left in plaintext storage or exposed in transit.
Clause 5.7 and Clause 5.13 - Integrity, logging, and monitoring. Audit records need integrity protection, and timestamps are part of that protected scope. The product shall record events for all relevant functions, privileged login attempts, and product updates, and the log records shall include the event time, event type, subject identity where applicable, and success or failure. The periodic signing of audit logs is used to make tampering detectable.
Clause 5.9 - Availability protection. The standard treats certificate status as part of availability protection. OCSP or CRL shall be supported, multiple status services shall remain consistent over time, CRLs shall carry the next scheduled issue time, and CA revocation shall trigger a new CARL. This keeps relying parties from using stale or unclear trust data.
Clause 5.11 - Minimisation of attack surfaces. Only the interfaces identified for the applicable use case in Annex U shall be implemented. For a product team, that means avoiding extra ports, services, APIs, maintenance channels, or test interfaces that widen exposure.
Clause 5.12 and Clause 5.14 - Certificate control and data removal. The document sets controls for certificate issuance, status, re-key, and modification, including profile constraints such as keyUsage, basicConstraints, and certificatePolicies where applicable. It also requires data removal and transparency, including secure deletion handling for secrets and protection of public keys stored outside an SCD.
What terms does oSIST prEN 304 624 V1.0.0:2026 define?
oSIST prEN 304 624 V1.0.0:2026 defines the core PKI terms used throughout the requirements and assessments.
- Public Key Infrastructure (PKI) - a system for managing public keys where private keys must remain secret.
- Certificate - a public key of a user, together with other information, rendered unforgeable by encipherment with the private key of the issuing CA.
- Certification Authority (CA) - an authority trusted by one or more users to create and assign certificates.
- Certificate Revocation List (CRL) - a signed list showing certificates that have been revoked by the issuer.
- Registration Authority (RA) - an entity responsible mainly for identifying and authenticating certificate subjects.
- secure cryptographic device (SCD) - a device that holds the user's private key, protects it against compromise, and performs signing or decryption on the user's behalf.
- Certificate Policy (CP) - a named set of rules that states where and how a certificate may be used.
- Use case (UC) - one of the scoping scenarios used to describe product functions, assets, interfaces, and security-function distribution.
Who uses oSIST prEN 304 624 V1.0.0:2026?
oSIST prEN 304 624 V1.0.0:2026 is used by people who build, operate, assess, or buy PKI software for private or public environments, especially where critical entities are involved.
The main user roles named in the document are the Product Administrator, Product Operator, and Officer or Registration Authority Officer. The Product Administrator installs, configures, and maintains the product; the Product Operator handles availability, backups, recovery, and routine operations; and the Officer manages certificate-lifecycle actions such as approvals, profile settings, and revocations.
Auditors also use the standard, because it requires traceable logging and controlled access to audit data. It is relevant to PKI software developers and integrators, certification authorities, registration authorities, trust service providers, and organisations that run private PKI, public PKI, or multi-authority PKI for critical entities.
Which standards are used with oSIST prEN 304 624 V1.0.0:2026?
The standard relies on a small set of external documents for cryptography, terminology, vulnerability handling, and legal context.
- ENISA Report 1747792503 - provides the agreed cryptographic mechanisms referenced by Annex K.
- Recommendation ITU-T X.509 - provides the certificate framework used for PKI and certificate-related requirements.
- prEN 40000-1-1 - supplies additional terms and definitions used by the standard.
- prEN 40000-1-3 - is referenced for the vulnerability handling process used when known exploitable vulnerabilities are assessed.
- Regulation (EU) 2024/2847, the Cyber Resilience Act (CRA) - is the legal framework the standard supports.
- Commission Implementing Regulation (EU) 2025/2392 - defines the product category used in the scope.
- Directive (EU) 2022/2557 - provides the definition of critical entities used in the document.
- NIST SP 800-130 - gives guidance for designing cryptographic key management systems.
- Regulation (EU) 2016/679 - provides the personal-data protection context for handling personal information.
What does the oSIST prEN 304 624 V1.0.0:2026 document contain?
oSIST prEN 304 624 V1.0.0:2026 contains an indicative product architecture, an assets figure, and a structured set of assessment criteria that tell the reader what evidence to collect. The assessment method is laid out in a repeatable form: objective, preparation, activities, evidence, and pass/fail verdict.
Annex A maps the technical clauses to CRA essential requirements. Annex B gives the security-analysis method, including impact and likelihood tables, risk evaluation, and threat-to-requirement mapping. Annex K develops the cryptographic side in more detail, including product cryptographic configuration, crypto agility, ACM-extended mechanisms, and interoperability-based mechanisms. Annex U expands the five use cases - UC1 to UC5 - with the functions, assets, operational environment, security-function distribution, and user roles needed for each scenario.
The body of the document also contains practical test and review material for certificate issuance, revocation, status services, logging, interface exposure, secure updates, and data removal. For an assessor, that means the standard is not just a list of requirements - it also shows how to check them with documentation review, configuration inspection, and functional testing.
Get Certified
Connect with accredited certification bodies for this standard

BSI Group
BSI (British Standards Institution) is the business standards company that helps organizations make excellence a habit.

Bureau Veritas
Bureau Veritas is a world leader in laboratory testing, inspection and certification services.

DNV
DNV is an independent assurance and risk management provider.
Sponsored listings
Frequently Asked Questions
oSIST prEN 304 624 V1.0.0:2026 is a standard published by the Slovenian Institute for Standardization (SIST). Its full title is "Cyber Security (CYBER) - CRA - Cybersecurity requirements for Public key infrastructure and digital certificate issuance software". This standard covers: DEN/CYBER-EUS-0015
DEN/CYBER-EUS-0015
oSIST prEN 304 624 V1.0.0:2026 is classified under the following ICS (International Classification for Standards) categories: 35.030 - IT Security. The ICS classification helps identify the subject area and facilitates finding related standards.
oSIST prEN 304 624 V1.0.0:2026 is available in PDF format for immediate download after purchase. The document can be added to your cart and obtained through the secure checkout process. Digital delivery ensures instant access to the complete standard document.
Standards Content (Sample)
Draft ETSI EN 304 624 V1.0.0 (2026-08)
HARMONISED EUROPEAN STANDARD
Cyber security (CYBER);
CRA;
Cybersecurity requirements for public key infrastructure and
digital certificate issuance software
2 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Reference
DEN/CYBER-EUS-0015
Keywords
certificate, CRA, cybersecurity, public key
infrastructure
ETSI
650 Route des Lucioles
F-06921 Sophia Antipolis Cedex - FRANCE
Tel.: +33 4 92 94 42 00 Fax: +33 4 93 65 47 16
Siret N° 348 623 562 00017 - APE 7112B
Association à but non lucratif enregistrée à la
Sous-Préfecture de Grasse (06) N° w061004871
Important notice
The present document can be downloaded from the
ETSI Search & Browse Standards application.
The present document may be made available in electronic versions and/or in print. The content of any electronic and/or
print versions of the present document shall not be modified without the prior written authorization of ETSI. In case of any
existing or perceived difference in contents between such versions and/or in print, the prevailing version of an ETSI
deliverable is the one made publicly available in PDF format on ETSI deliver repository.
Users should be aware that the present document may be revised or have its status changed,
this information is available in the Milestones listing.
If you find errors in the present document, please send your comments to
the relevant service listed under Committee Support Staff.
If you find a security vulnerability in the present document, please report it through our
Coordinated Vulnerability Disclosure (CVD) program.
Notice of disclaimer & limitation of liability
The information provided in the present deliverable is directed solely to professionals who have the appropriate degree of
experience to understand and interpret its content in accordance with generally accepted engineering or
other professional standard and applicable regulations.
No recommendation as to products and services or vendors is made or should be implied.
In no event shall ETSI be held liable for loss of profits or any other incidental or consequential damages.
Any software contained in this deliverable is provided "AS IS" with no warranties, express or implied, including but not
limited to, the warranties of merchantability, fitness for a particular purpose and non-infringement of intellectual property
rights and ETSI shall not be held liable in any event for any damages whatsoever (including, without limitation, damages
for loss of profits, business interruption, loss of information, or any other pecuniary loss) arising out of or related to the use
of or inability to use the software.
Copyright Notification
No part of this document may be reproduced in any form, by any means and in any media, without the prior written
authorization of ETSI and except as expressly permitted below.
By way of exception and when the document is a normative deliverable (European Standard (EN),
Technical Specification (TS), Group Specification (GS) or ETSI Standard (ES)), ETSI authorizes to reproduce
and incorporate into products, services and technical documentation only those extracts (e.g. templates) that are strictly
necessary for the technical implementation of the normative deliverable, to ensure compliance with the latter.
Nothing in this notice shall be construed as limiting any mandatory exceptions to copyright provided by applicable law.
© ETSI 2026.
All rights reserved.
ETSI
3 Draft ETSI EN 304 624 V1.0.0 (2026-08)
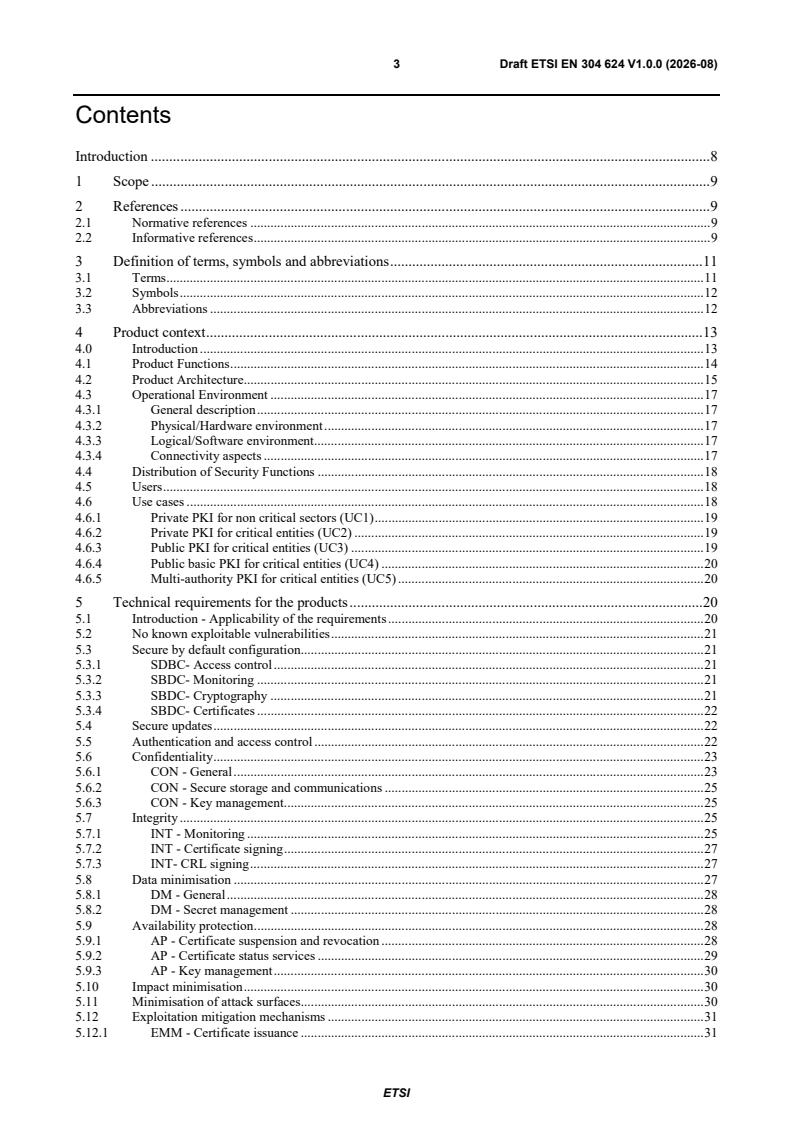
Contents
Introduction . 8
1 Scope . 9
2 References . 9
2.1 Normative references . 9
2.2 Informative references . 9
3 Definition of terms, symbols and abbreviations . 11
3.1 Terms . 11
3.2 Symbols . 12
3.3 Abbreviations . 12
4 Product context . 13
4.0 Introduction . 13
4.1 Product Functions . 14
4.2 Product Architecture. 15
4.3 Operational Environment . 17
4.3.1 General description . 17
4.3.2 Physical/Hardware environment . 17
4.3.3 Logical/Software environment. 17
4.3.4 Connectivity aspects . 17
4.4 Distribution of Security Functions . 18
4.5 Users . 18
4.6 Use cases . 18
4.6.1 Private PKI for non critical sectors (UC1) . 19
4.6.2 Private PKI for critical entities (UC2) . 19
4.6.3 Public PKI for critical entities (UC3) . 19
4.6.4 Public basic PKI for critical entities (UC4) . 20
4.6.5 Multi-authority PKI for critical entities (UC5) . 20
5 Technical requirements for the products . 20
5.1 Introduction - Applicability of the requirements . 20
5.2 No known exploitable vulnerabilities . 21
5.3 Secure by default configuration . 21
5.3.1 SDBC- Access control . 21
5.3.2 SBDC- Monitoring . 21
5.3.3 SBDC- Cryptography . 21
5.3.4 SBDC- Certificates . 22
5.4 Secure updates . 22
5.5 Authentication and access control . 22
5.6 Confidentiality . 23
5.6.1 CON - General . 23
5.6.2 CON - Secure storage and communications . 25
5.6.3 CON - Key management . 25
5.7 Integrity . 25
5.7.1 INT - Monitoring . 25
5.7.2 INT - Certificate signing . 27
5.7.3 INT- CRL signing . 27
5.8 Data minimisation . 27
5.8.1 DM - General . 28
5.8.2 DM - Secret management . 28
5.9 Availability protection . 28
5.9.1 AP - Certificate suspension and revocation . 28
5.9.2 AP - Certificate status services . 29
5.9.3 AP - Key management . 30
5.10 Impact minimisation . 30
5.11 Minimisation of attack surfaces . 30
5.12 Exploitation mitigation mechanisms . 31
5.12.1 EMM - Certificate issuance . 31
ETSI
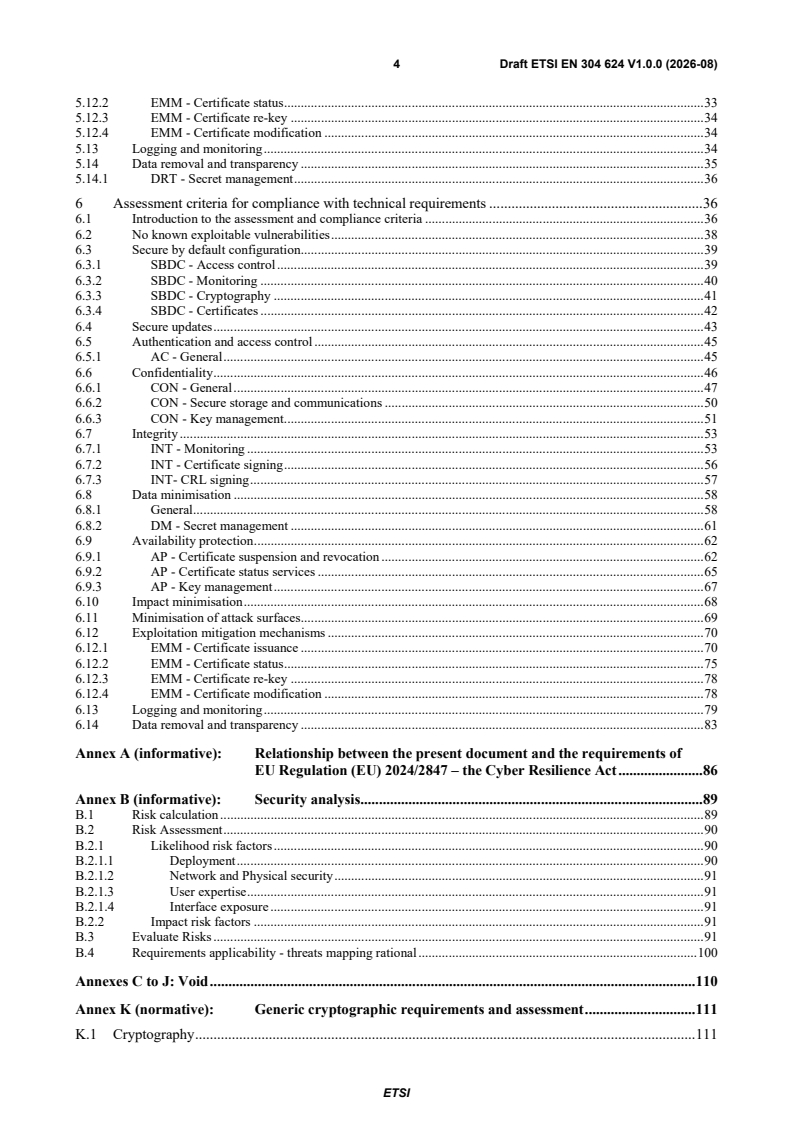
4 Draft ETSI EN 304 624 V1.0.0 (2026-08)
5.12.2 EMM - Certificate status . 33
5.12.3 EMM - Certificate re-key . 34
5.12.4 EMM - Certificate modification . 34
5.13 Logging and monitoring . 34
5.14 Data removal and transparency . 35
5.14.1 DRT - Secret management . 36
6 Assessment criteria for compliance with technical requirements . 36
6.1 Introduction to the assessment and compliance criteria . 36
6.2 No known exploitable vulnerabilities . 38
6.3 Secure by default configuration . 39
6.3.1 SBDC - Access control . 39
6.3.2 SBDC - Monitoring . 40
6.3.3 SBDC - Cryptography . 41
6.3.4 SBDC - Certificates . 42
6.4 Secure updates . 43
6.5 Authentication and access control . 45
6.5.1 AC - General . 45
6.6 Confidentiality . 46
6.6.1 CON - General . 47
6.6.2 CON - Secure storage and communications . 50
6.6.3 CON - Key management . 51
6.7 Integrity . 53
6.7.1 INT - Monitoring . 53
6.7.2 INT - Certificate signing . 56
6.7.3 INT- CRL signing . 57
6.8 Data minimisation . 58
6.8.1 General . 58
6.8.2 DM - Secret management . 61
6.9 Availability protection . 62
6.9.1 AP - Certificate suspension and revocation . 62
6.9.2 AP - Certificate status services . 65
6.9.3 AP - Key management . 67
6.10 Impact minimisation . 68
6.11 Minimisation of attack surfaces . 69
6.12 Exploitation mitigation mechanisms . 70
6.12.1 EMM - Certificate issuance . 70
6.12.2 EMM - Certificate status . 75
6.12.3 EMM - Certificate re-key . 78
6.12.4 EMM - Certificate modification . 78
6.13 Logging and monitoring . 79
6.14 Data removal and transparency . 83
Annex A (informative): Relationship between the present document and the requirements of
EU Regulation (EU) 2024/2847 – the Cyber Resilience Act . 86
Annex B (informative): Security analysis . 89
B.1 Risk calculation . 89
B.2 Risk Assessment . 90
B.2.1 Likelihood risk factors . 90
B.2.1.1 Deployment . 90
B.2.1.2 Network and Physical security . 91
B.2.1.3 User expertise . 91
B.2.1.4 Interface exposure . 91
B.2.2 Impact risk factors . 91
B.3 Evaluate Risks . 91
B.4 Requirements applicability - threats mapping rational . 100
Annexes C to J: Void . 110
Annex K (normative): Generic cryptographic requirements and assessment . 111
K.1 Cryptography . 111
ETSI
5 Draft ETSI EN 304 624 V1.0.0 (2026-08)
K.1.1 Requirement . 111
K.1.2 Assessment of product cryptographic configuration . 112
K.1.2.0 General . 112
K.1.2.1 Assessment of ACM-listed cryptographic mechanisms. 112
K.1.2.1.1 Assessment objective . 112
K.1.2.1.2 Assessment preparation . 112
K.1.2.1.3 Assessment activities . 112
K.1.2.1.4 Assessment evidence . 112
K.1.2.1.5 Assessment verdict . 113
K.1.2.2 Assessment of ACM-extended cryptographic mechanisms . 113
K.1.2.2.1 Assessment objective . 113
K.1.2.2.2 Assessment preparation . 113
K.1.2.2.3 Assessment activities . 113
K.1.2.2.4 Assessment evidence . 114
K.1.2.2.5 Assessment verdict . 114
K.1.2.3 Assessment of interoperability-based cryptographic mechanisms . 114
K.1.2.3.1 Assessment objective . 114
K.1.2.3.2 Assessment preparation . 114
K.1.2.3.3 Assessment activities . 114
K.1.2.3.4 Assessment evidence . 115
K.1.2.3.5 Assessment verdict . 115
K.2 Crypto agility . 115
K.2.1 Requirement . 115
K.2.2 Assessment of crypto-agility . 116
K.2.2.1 Assessment objective . 116
K.2.2.2 Assessment preparation . 116
K.2.2.3 Assessment activities . 117
K.2.2.4 Assessment evidence . 117
K.2.2.5 Assessment verdict . 117
K.3 ACM-extended cryptographic mechanisms . 117
K.3.1 Requirement . 117
K.3.2 List of ACM-extended cryptographic mechanisms . 118
K.3.3 Assessment . 118
K.4 Interoperability-based cryptographic mechanisms . 118
K.4.1 Requirement . 118
K.4.2 List of interoperability-based cryptographic mechanisms . 118
K.4.3 Assessment . 118
Annexes I to T: Void . 119
Annex U (informative): Use case description . 120
U.1 UC1 - Product for use in Private PKI for non critical sectors . 120
U.1.1 UC1 - General description . 120
U.1.2 UC1 - Product Functions and assets . 122
U.1.2.1 UC1 - List of functions . 122
U.1.2.2 UC1 - Assets . 123
U.1.3 UC1 - Operational Environment . 123
U.1.4 UC1 - Distribution of Security Functions. 123
U.1.5 UC1 - Users . 124
U.2 UC2 - Product for use in Private PKI for critical entities . 124
U.2.1 UC2 - General description . 124
U.2.2 UC2 - List of functions . 126
U.2.2.1 UC2 - Assets . 127
U.2.3 UC2 - Operational Environment . 127
U.2.4 UC2 - Distribution of Security Functions. 128
U.2.5 UC2 - Users . 128
U.3 UC3 - Public PKI for critical entities . 128
U.3.1 General description. 128
ETSI
6 Draft ETSI EN 304 624 V1.0.0 (2026-08)
U.3.2 UC3 - List of functions . 129
U.3.2.1 UC3 - Assets . 130
U.3.3 UC3 - Operational Environment . 130
U.3.4 UC3 - Distribution of Security Functions. 131
U.3.5 UC3 - Users . 131
U.4 UC4 - Product for use in Critical Public basic PKI . 131
U.4.1 UC4 - General description . 131
U.4.2 UC4 - List of functions . 133
U.4.2.1 UC4 - Assets . 133
U.4.3 UC4 - Operational Environment . 134
U.4.4 UC4 - Distribution of Security Functions. 134
U.4.5 UC4 - Users . 134
U.5 UC5 - Product for use in Critical Multi-Authority PKI . 134
U.5.1 General description. 134
U.5.2 UC5 - List of functions . 136
U.5.2.1 UC5 - Assets . 137
U.5.3 UC5 - Operational Environment . 138
U.5.4 UC5 - Distribution of Security Functions. 138
U.5.5 UC5 - Users . 138
Annex V (informative): Change history . 139
History . 141
ETSI
7 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Intellectual Property Rights
Essential patents
IPRs essential or potentially essential to normative deliverables (European Standard (EN), Technical Specification (TS),
Group Specification (GS) or ETSI Standard (ES)) may have been declared to ETSI. The declarations pertaining to these
essential IPRs, if any, are publicly available for ETSI members and non-members, and can be found in
ETSI SR 000 314: "Intellectual Property Rights (IPRs); Essential, or potentially Essential, IPRs notified to ETSI in
respect of ETSI standards", which is available from the ETSI Secretariat. Latest updates are available on the
ETSI IPR online database.
Pursuant to the ETSI Directives including the ETSI IPR Policy, no investigation regarding the essentiality of IPRs,
including IPR searches, has been carried out by ETSI. No guarantee can be given as to the existence of other IPRs not
referenced in ETSI SR 000 314 (or the updates on the ETSI Web server) which are, or may be, or may become,
essential to the present document.
Trademarks
The present document may include trademarks and/or tradenames which are asserted and/or registered by their owners.
ETSI claims no ownership of these except for any which are indicated as being the property of ETSI, and conveys no
right to use or reproduce any trademark and/or tradename. Mention of those trademarks in the present document does
not constitute an endorsement by ETSI of products, services or organizations associated with those trademarks.
DECT™, PLUGTESTS™, UMTS™ and the ETSI logo are trademarks of ETSI registered for the benefit of its
Members. 3GPP™, LTE™ and 5G™ logo are trademarks of ETSI registered for the benefit of its Members and of the
3GPP Organizational Partners. oneM2M™ logo is a trademark of ETSI registered for the benefit of its Members and of ®
the oneM2M Partners. GSM and the GSM logo are trademarks registered and owned by the GSM Association.
Foreword
This draft Harmonised European Standard (EN) has been produced by ETSI Technical Committee Cyber Security
(CYBER), and is now submitted for the combined Public Enquiry and Vote phase of the ETSI Standardisation Request
deliverable Approval Procedure (SRdAP).
The present document has been prepared under the Commission's Standardisation request M/606 - C(2025)618 [i.3] to
provide one voluntary means of conforming to the requirements of EU Regulation No 2024/2847 of the European
Parliament and of the Council of 23 October 2024 on horizontal cybersecurity requirements for products with digital
elements and amending Regulations (EU) No 168/2013 and (EU) No 2019/1020 and Directive (EU) 2020/1828 (Cyber
Resilience Act) (CRA) [i.1].
Once the present document is cited in the Official Journal of the European Union under that Regulation, compliance
with the normative clauses of the present document given in Table A.1 confers, within the limits of the scope of the
present document, a presumption of conformity with the corresponding requirements of that Regulation and associated
EFTA regulations.
Proposed national transposition dates
Date of latest announcement of this EN (doa): 3 months after ETSI publication
Date of latest publication of new National Standard
or endorsement of this EN (dop/e): 6 months after doa
Date of withdrawal of any conflicting National Standard (dow): 18 months after doa
ETSI
8 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Modal verbs terminology
In the present document "shall", "shall not", "should", "should not", "may", "need not", "will", "will not", "can" and
"cannot" are to be interpreted as described in clause 3.2 of the ETSI Drafting Rules (Verbal forms for the expression of
provisions).
"must" and "must not" are NOT allowed in ETSI deliverables except when used in direct citation.
Introduction
The present document provides the technical cybersecurity requirements for the products in scope, following a risk-
based approach in support of the Cyber Resilience Act (CRA) [i.1]. The technical cybersecurity requirements are
thereby proportionate to the intended purpose, reasonably foreseeable use, deployment context, and threat exposure of
the products.
Clause 4 does not contain technical requirements; it describes the product context that is considered for the application
of the present document.
Clause 4 also defines Use Cases (UCs) that represent the main deployment scenarios reflecting the intended purpose
and reasonably foreseeable use of the product, which serve as the basis for identifying relevant cybersecurity risks.
Clause 5 specifies technical cybersecurity requirements for the product to mitigate the identified risks, including their
applicability conditions.
Clause 6 specifies the assessment criteria and compliance verification procedures with the requirements of Clause 5.
Annex A maps the technical requirements of the present document with the essential requirements of the CRA [i.1]
regulation.
Annex B informs about the methodology used to assess the security risks of the products in their context.
Annex K supports the definition of the cryptographic requirements and assessment criteria used by the present
document.
Annex U defines in more details the use cases contexts and parameters.
ETSI
9 Draft ETSI EN 304 624 V1.0.0 (2026-08)
1 Scope
The present document specifies technical requirements and corresponding assessment criteria for public key
infrastructure and digital certificate issuance software related to cybersecurity. The products with digital elements in
scope, thereafter "the Products":
• are specified within the "technical description" of the "category of product" number "9" by the Commission
Implementing Regulation (EU) 2025/2392 [i.2] as:
"Products with digital elements used as part of a public key infrastructure (PKI) that manage the validation,
creation, issuance, distribution, status publication, renewal or revocation of digital certificates, or the
generation, storage, escrow, exchange, destruction or rotation of cryptographic keys associated with such
digital certificates. This category includes but is not limited to key management systems, digital certificate
management systems, online certificate status protocol responders and all-in-one PKI solutions".
• are only covered within the product context described in clause 4.
The present document covers those Products to demonstrate compliance with essential cybersecurity requirements in
the Regulation (EU) 2024/2847 [i.1] Annex I Part I under the conditions identified in annex A.
Different use cases representing different product architecture are presented in clause 4.6. Requirements applicability in
clause 5 then defines which requirements apply to which use case to ensure compliance with the CRA's essential
cybersecurity requirements.
2 References
2.1 Normative references
References are either specific (identified by date of publication and/or edition number or version number) or
non-specific. For specific references, only the cited version applies. For non-specific references, the latest version of the
referenced document (including any amendments) applies.
Referenced documents which are not found to be publicly available in the expected location might be found in the
ETSI docbox.
NOTE: While any hyperlinks included in this clause were valid at the time of publication, ETSI cannot guarantee
their long-term validity.
The following referenced documents are necessary for the application of the present document.
[1] ENISA Report 1747792503: "European Cybersecurity Certification Group Sub-group on
Cryptography Agreed Cryptographic Mechanisms - version 2" – April 2025.
[2] Recommendation ITU-T X.509 (10/2019): "Information technology - Open Systems
Interconnection - The Directory: Public-key and attribute certificate frameworks".
NOTE: Identical text in the defining of public-key and attribute certificates is also available in ISO/IEC 9594‑8
(paywall).
[3] IEEE Std 1609.2™-2025" "(2025): "Standard for Wireless Access in Vehicular Environments -
Security Services for Applications and Management Messages".
[4] IETF RFC 6960 (June 2013): "X.509 Internet Public Key Infrastructure Online Certificate Status
Protocol - OCSP".
2.2 Informative references
References are either specific (identified by date of publication and/or edition number or version number) or
nonspecific. For specific references, only the cited version applies. For non-specific references, the latest version of the
referenced document (including any amendments) applies.
ETSI
10 Draft ETSI EN 304 624 V1.0.0 (2026-08)
NOTE: While any hyperlinks included in this clause were valid at the time of publication, ETSI cannot guarantee
their long term validity.
The following referenced documents may be useful in implementing an ETSI deliverable or add to the reader's
understanding but are not required for conformance to the present document.
[i.1] Regulation (EU) 2024/2847 of the European Parliament and of the Council of 23 October 2024 on
horizontal cybersecurity requirements for products with digital elements and amending
Regulations (EU) No 168/2013 and (EU) 2019/1020 and Directive (EU) 2020/1828 (Cyber
Resilience Act).
[i.2] Commission Implementing Regulation (EU) 2025/2392 of 28 November 2025 on the technical
description of the categories of important and critical products with digital elements pursuant to
Regulation (EU) 2024/2847 of the European Parliament and of the Council.
[i.3] Standardisation request M/606 - C(2025)618: "Commission Implementing decision of 3.2.2025 on
a standardisation request to the European Committee for Standardisation (CEN), the European
Committee for Electrotechnical Standardisation (Cenelec) and the European Telecommunications
Standards Institute (ETSI) as regards products with digital elements in support of Regulation (EU)
2024/2847 of the European Parliament and of the Council of 23 October 2024 on horizontal
cybersecurity requirements for products with digital elements and amending Regulations (EU) No
168/2013 and (EU) 2019/1020and Directive (EU) 2020/1828 (Cyber Resilience Act)".
[i.4] prEN 40000-1-1: "Cybersecurity requirements for products with digital elements - Vocabulary",
produced by CEN CENELEC.
NOTE: Version and date to be added upon its publication by CEN CENELEC.
[i.5] IETF RFC 4120: "The Kerberos Network Authentication Service (V5) - July 2005".
[i.6] ETSI GS NFV 003 (V1.4.1) (2018-08): "Network Functions Virtualisation (NFV); Terminology
for Main Concepts in NFV".
[i.7] ETSI TS 102 941 (V2.2.1) (11-2022): "Intelligent Transport Systems (ITS); Security; Trust and
Privacy Management; Re
...
SLOVENSKI STANDARD
01-oktober-2026
Kibernetska varnost (CYBER) - CRA - Zahteve za kibernetsko varnost za
infrastrukturo javnih ključev in programsko opremo za izdajanje digitalnih potrdil
Cyber Security (CYBER) - CRA - Cybersecurity requirements for Public key
infrastructure and digital certificate issuance software
Ta slovenski standard je istoveten z: ETSI EN 304 624 V1.0.0 (2026-08)
ICS:
35.030 Informacijska varnost IT Security
2003-01.Slovenski inštitut za standardizacijo. Razmnoževanje celote ali delov tega standarda ni dovoljeno.
Draft ETSI EN 304 624 V1.0.0 (2026-08)
HARMONISED EUROPEAN STANDARD
Cyber security (CYBER);
CRA;
Cybersecurity requirements for public key infrastructure and
digital certificate issuance software
2 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Reference
DEN/CYBER-EUS-0015
Keywords
certificate, CRA, cybersecurity, public key
infrastructure
ETSI
650 Route des Lucioles
F-06921 Sophia Antipolis Cedex - FRANCE
Tel.: +33 4 92 94 42 00 Fax: +33 4 93 65 47 16
Siret N° 348 623 562 00017 - APE 7112B
Association à but non lucratif enregistrée à la
Sous-Préfecture de Grasse (06) N° w061004871
Important notice
The present document can be downloaded from the
ETSI Search & Browse Standards application.
The present document may be made available in electronic versions and/or in print. The content of any electronic and/or
print versions of the present document shall not be modified without the prior written authorization of ETSI. In case of any
existing or perceived difference in contents between such versions and/or in print, the prevailing version of an ETSI
deliverable is the one made publicly available in PDF format on ETSI deliver repository.
Users should be aware that the present document may be revised or have its status changed,
this information is available in the Milestones listing.
If you find errors in the present document, please send your comments to
the relevant service listed under Committee Support Staff.
If you find a security vulnerability in the present document, please report it through our
Coordinated Vulnerability Disclosure (CVD) program.
Notice of disclaimer & limitation of liability
The information provided in the present deliverable is directed solely to professionals who have the appropriate degree of
experience to understand and interpret its content in accordance with generally accepted engineering or
other professional standard and applicable regulations.
No recommendation as to products and services or vendors is made or should be implied.
In no event shall ETSI be held liable for loss of profits or any other incidental or consequential damages.
Any software contained in this deliverable is provided "AS IS" with no warranties, express or implied, including but not
limited to, the warranties of merchantability, fitness for a particular purpose and non-infringement of intellectual property
rights and ETSI shall not be held liable in any event for any damages whatsoever (including, without limitation, damages
for loss of profits, business interruption, loss of information, or any other pecuniary loss) arising out of or related to the use
of or inability to use the software.
Copyright Notification
No part of this document may be reproduced in any form, by any means and in any media, without the prior written
authorization of ETSI and except as expressly permitted below.
By way of exception and when the document is a normative deliverable (European Standard (EN),
Technical Specification (TS), Group Specification (GS) or ETSI Standard (ES)), ETSI authorizes to reproduce
and incorporate into products, services and technical documentation only those extracts (e.g. templates) that are strictly
necessary for the technical implementation of the normative deliverable, to ensure compliance with the latter.
Nothing in this notice shall be construed as limiting any mandatory exceptions to copyright provided by applicable law.
© ETSI 2026.
All rights reserved.
ETSI
3 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Contents
Introduction . 8
1 Scope . 9
2 References . 9
2.1 Normative references . 9
2.2 Informative references . 9
3 Definition of terms, symbols and abbreviations . 11
3.1 Terms . 11
3.2 Symbols . 12
3.3 Abbreviations . 12
4 Product context . 13
4.0 Introduction . 13
4.1 Product Functions . 14
4.2 Product Architecture. 15
4.3 Operational Environment . 17
4.3.1 General description . 17
4.3.2 Physical/Hardware environment . 17
4.3.3 Logical/Software environment. 17
4.3.4 Connectivity aspects . 17
4.4 Distribution of Security Functions . 18
4.5 Users . 18
4.6 Use cases . 18
4.6.1 Private PKI for non critical sectors (UC1) . 19
4.6.2 Private PKI for critical entities (UC2) . 19
4.6.3 Public PKI for critical entities (UC3) . 19
4.6.4 Public basic PKI for critical entities (UC4) . 20
4.6.5 Multi-authority PKI for critical entities (UC5) . 20
5 Technical requirements for the products . 20
5.1 Introduction - Applicability of the requirements . 20
5.2 No known exploitable vulnerabilities . 21
5.3 Secure by default configuration . 21
5.3.1 SDBC- Access control . 21
5.3.2 SBDC- Monitoring . 21
5.3.3 SBDC- Cryptography . 21
5.3.4 SBDC- Certificates . 22
5.4 Secure updates . 22
5.5 Authentication and access control . 22
5.6 Confidentiality . 23
5.6.1 CON - General . 23
5.6.2 CON - Secure storage and communications . 25
5.6.3 CON - Key management . 25
5.7 Integrity . 25
5.7.1 INT - Monitoring . 25
5.7.2 INT - Certificate signing . 27
5.7.3 INT- CRL signing . 27
5.8 Data minimisation . 27
5.8.1 DM - General . 28
5.8.2 DM - Secret management . 28
5.9 Availability protection . 28
5.9.1 AP - Certificate suspension and revocation . 28
5.9.2 AP - Certificate status services . 29
5.9.3 AP - Key management . 30
5.10 Impact minimisation . 30
5.11 Minimisation of attack surfaces . 30
5.12 Exploitation mitigation mechanisms . 31
5.12.1 EMM - Certificate issuance . 31
ETSI
4 Draft ETSI EN 304 624 V1.0.0 (2026-08)
5.12.2 EMM - Certificate status . 33
5.12.3 EMM - Certificate re-key . 34
5.12.4 EMM - Certificate modification . 34
5.13 Logging and monitoring . 34
5.14 Data removal and transparency . 35
5.14.1 DRT - Secret management . 36
6 Assessment criteria for compliance with technical requirements . 36
6.1 Introduction to the assessment and compliance criteria . 36
6.2 No known exploitable vulnerabilities . 38
6.3 Secure by default configuration . 39
6.3.1 SBDC - Access control . 39
6.3.2 SBDC - Monitoring . 40
6.3.3 SBDC - Cryptography . 41
6.3.4 SBDC - Certificates . 42
6.4 Secure updates . 43
6.5 Authentication and access control . 45
6.5.1 AC - General . 45
6.6 Confidentiality . 46
6.6.1 CON - General . 47
6.6.2 CON - Secure storage and communications . 50
6.6.3 CON - Key management . 51
6.7 Integrity . 53
6.7.1 INT - Monitoring . 53
6.7.2 INT - Certificate signing . 56
6.7.3 INT- CRL signing . 57
6.8 Data minimisation . 58
6.8.1 General . 58
6.8.2 DM - Secret management . 61
6.9 Availability protection . 62
6.9.1 AP - Certificate suspension and revocation . 62
6.9.2 AP - Certificate status services . 65
6.9.3 AP - Key management . 67
6.10 Impact minimisation . 68
6.11 Minimisation of attack surfaces . 69
6.12 Exploitation mitigation mechanisms . 70
6.12.1 EMM - Certificate issuance . 70
6.12.2 EMM - Certificate status . 75
6.12.3 EMM - Certificate re-key . 78
6.12.4 EMM - Certificate modification . 78
6.13 Logging and monitoring . 79
6.14 Data removal and transparency . 83
Annex A (informative): Relationship between the present document and the requirements of
EU Regulation (EU) 2024/2847 – the Cyber Resilience Act . 86
Annex B (informative): Security analysis . 89
B.1 Risk calculation . 89
B.2 Risk Assessment . 90
B.2.1 Likelihood risk factors . 90
B.2.1.1 Deployment . 90
B.2.1.2 Network and Physical security . 91
B.2.1.3 User expertise . 91
B.2.1.4 Interface exposure . 91
B.2.2 Impact risk factors . 91
B.3 Evaluate Risks . 91
B.4 Requirements applicability - threats mapping rational . 100
Annexes C to J: Void . 110
Annex K (normative): Generic cryptographic requirements and assessment . 111
K.1 Cryptography . 111
ETSI
5 Draft ETSI EN 304 624 V1.0.0 (2026-08)
K.1.1 Requirement . 111
K.1.2 Assessment of product cryptographic configuration . 112
K.1.2.0 General . 112
K.1.2.1 Assessment of ACM-listed cryptographic mechanisms. 112
K.1.2.1.1 Assessment objective . 112
K.1.2.1.2 Assessment preparation . 112
K.1.2.1.3 Assessment activities . 112
K.1.2.1.4 Assessment evidence . 112
K.1.2.1.5 Assessment verdict . 113
K.1.2.2 Assessment of ACM-extended cryptographic mechanisms . 113
K.1.2.2.1 Assessment objective . 113
K.1.2.2.2 Assessment preparation . 113
K.1.2.2.3 Assessment activities . 113
K.1.2.2.4 Assessment evidence . 114
K.1.2.2.5 Assessment verdict . 114
K.1.2.3 Assessment of interoperability-based cryptographic mechanisms . 114
K.1.2.3.1 Assessment objective . 114
K.1.2.3.2 Assessment preparation . 114
K.1.2.3.3 Assessment activities . 114
K.1.2.3.4 Assessment evidence . 115
K.1.2.3.5 Assessment verdict . 115
K.2 Crypto agility . 115
K.2.1 Requirement . 115
K.2.2 Assessment of crypto-agility . 116
K.2.2.1 Assessment objective . 116
K.2.2.2 Assessment preparation . 116
K.2.2.3 Assessment activities . 117
K.2.2.4 Assessment evidence . 117
K.2.2.5 Assessment verdict . 117
K.3 ACM-extended cryptographic mechanisms . 117
K.3.1 Requirement . 117
K.3.2 List of ACM-extended cryptographic mechanisms . 118
K.3.3 Assessment . 118
K.4 Interoperability-based cryptographic mechanisms . 118
K.4.1 Requirement . 118
K.4.2 List of interoperability-based cryptographic mechanisms . 118
K.4.3 Assessment . 118
Annexes I to T: Void . 119
Annex U (informative): Use case description . 120
U.1 UC1 - Product for use in Private PKI for non critical sectors . 120
U.1.1 UC1 - General description . 120
U.1.2 UC1 - Product Functions and assets . 122
U.1.2.1 UC1 - List of functions . 122
U.1.2.2 UC1 - Assets . 123
U.1.3 UC1 - Operational Environment . 123
U.1.4 UC1 - Distribution of Security Functions. 123
U.1.5 UC1 - Users . 124
U.2 UC2 - Product for use in Private PKI for critical entities . 124
U.2.1 UC2 - General description . 124
U.2.2 UC2 - List of functions . 126
U.2.2.1 UC2 - Assets . 127
U.2.3 UC2 - Operational Environment . 127
U.2.4 UC2 - Distribution of Security Functions. 128
U.2.5 UC2 - Users . 128
U.3 UC3 - Public PKI for critical entities . 128
U.3.1 General description. 128
ETSI
6 Draft ETSI EN 304 624 V1.0.0 (2026-08)
U.3.2 UC3 - List of functions . 129
U.3.2.1 UC3 - Assets . 130
U.3.3 UC3 - Operational Environment . 130
U.3.4 UC3 - Distribution of Security Functions. 131
U.3.5 UC3 - Users . 131
U.4 UC4 - Product for use in Critical Public basic PKI . 131
U.4.1 UC4 - General description . 131
U.4.2 UC4 - List of functions . 133
U.4.2.1 UC4 - Assets . 133
U.4.3 UC4 - Operational Environment . 134
U.4.4 UC4 - Distribution of Security Functions. 134
U.4.5 UC4 - Users . 134
U.5 UC5 - Product for use in Critical Multi-Authority PKI . 134
U.5.1 General description. 134
U.5.2 UC5 - List of functions . 136
U.5.2.1 UC5 - Assets . 137
U.5.3 UC5 - Operational Environment . 138
U.5.4 UC5 - Distribution of Security Functions. 138
U.5.5 UC5 - Users . 138
Annex V (informative): Change history . 139
History . 141
ETSI
7 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Intellectual Property Rights
Essential patents
IPRs essential or potentially essential to normative deliverables (European Standard (EN), Technical Specification (TS),
Group Specification (GS) or ETSI Standard (ES)) may have been declared to ETSI. The declarations pertaining to these
essential IPRs, if any, are publicly available for ETSI members and non-members, and can be found in
ETSI SR 000 314: "Intellectual Property Rights (IPRs); Essential, or potentially Essential, IPRs notified to ETSI in
respect of ETSI standards", which is available from the ETSI Secretariat. Latest updates are available on the
ETSI IPR online database.
Pursuant to the ETSI Directives including the ETSI IPR Policy, no investigation regarding the essentiality of IPRs,
including IPR searches, has been carried out by ETSI. No guarantee can be given as to the existence of other IPRs not
referenced in ETSI SR 000 314 (or the updates on the ETSI Web server) which are, or may be, or may become,
essential to the present document.
Trademarks
The present document may include trademarks and/or tradenames which are asserted and/or registered by their owners.
ETSI claims no ownership of these except for any which are indicated as being the property of ETSI, and conveys no
right to use or reproduce any trademark and/or tradename. Mention of those trademarks in the present document does
not constitute an endorsement by ETSI of products, services or organizations associated with those trademarks.
DECT™, PLUGTESTS™, UMTS™ and the ETSI logo are trademarks of ETSI registered for the benefit of its
Members. 3GPP™, LTE™ and 5G™ logo are trademarks of ETSI registered for the benefit of its Members and of the
3GPP Organizational Partners. oneM2M™ logo is a trademark of ETSI registered for the benefit of its Members and of ®
the oneM2M Partners. GSM and the GSM logo are trademarks registered and owned by the GSM Association.
Foreword
This draft Harmonised European Standard (EN) has been produced by ETSI Technical Committee Cyber Security
(CYBER), and is now submitted for the combined Public Enquiry and Vote phase of the ETSI Standardisation Request
deliverable Approval Procedure (SRdAP).
The present document has been prepared under the Commission's Standardisation request M/606 - C(2025)618 [i.3] to
provide one voluntary means of conforming to the requirements of EU Regulation No 2024/2847 of the European
Parliament and of the Council of 23 October 2024 on horizontal cybersecurity requirements for products with digital
elements and amending Regulations (EU) No 168/2013 and (EU) No 2019/1020 and Directive (EU) 2020/1828 (Cyber
Resilience Act) (CRA) [i.1].
Once the present document is cited in the Official Journal of the European Union under that Regulation, compliance
with the normative clauses of the present document given in Table A.1 confers, within the limits of the scope of the
present document, a presumption of conformity with the corresponding requirements of that Regulation and associated
EFTA regulations.
Proposed national transposition dates
Date of latest announcement of this EN (doa): 3 months after ETSI publication
Date of latest publication of new National Standard
or endorsement of this EN (dop/e): 6 months after doa
Date of withdrawal of any conflicting National Standard (dow): 18 months after doa
ETSI
8 Draft ETSI EN 304 624 V1.0.0 (2026-08)
Modal verbs terminology
In the present document "shall", "shall not", "should", "should not", "may", "need not", "will", "will not", "can" and
"cannot" are to be interpreted as described in clause 3.2 of the ETSI Drafting Rules (Verbal forms for the expression of
provisions).
"must" and "must not" are NOT allowed in ETSI deliverables except when used in direct citation.
Introduction
The present document provides the technical cybersecurity requirements for the products in scope, following a risk-
based approach in support of the Cyber Resilience Act (CRA) [i.1]. The technical cybersecurity requirements are
thereby proportionate to the intended purpose, reasonably foreseeable use, deployment context, and threat exposure of
the products.
Clause 4 does not contain technical requirements; it describes the product context that is considered for the application
of the present document.
Clause 4 also defines Use Cases (UCs) that represent the main deployment scenarios reflecting the intended purpose
and reasonably foreseeable use of the product, which serve as the basis for identifying relevant cybersecurity risks.
Clause 5 specifies technical cybersecurity requirements for the product to mitigate the identified risks, including their
applicability conditions.
Clause 6 specifies the assessment criteria and compliance verification procedures with the requirements of Clause 5.
Annex A maps the technical requirements of the present document with the essential requirements of the CRA [i.1]
regulation.
Annex B informs about the methodology used to assess the security risks of the products in their context.
Annex K supports the definition of the cryptographic requirements and assessment criteria used by the present
document.
Annex U defines in more details the use cases contexts and parameters.
ETSI
9 Draft ETSI EN 304 624 V1.0.0 (2026-08)
1 Scope
The present document specifies technical requirements and corresponding assessment criteria for public key
infrastructure and digital certificate issuance software related to cybersecurity. The products with digital elements in
scope, thereafter "the Products":
• are specified within the "technical description" of the "category of product" number "9" by the Commission
Implementing Regulation (EU) 2025/2392 [i.2] as:
"Products with digital elements used as part of a public key infrastructure (PKI) that manage the validation,
creation, issuance, distribution, status publication, renewal or revocation of digital certificates, or the
generation, storage, escrow, exchange, destruction or rotation of cryptographic keys associated with such
digital certificates. This category includes but is not limited to key management systems, digital certificate
management systems, online certificate status protocol responders and all-in-one PKI solutions".
• are only covered within the product context described in clause 4.
The present document covers those Products to demonstrate compliance with essential cybersecurity requirements in
the Regulation (EU) 2024/2847 [i.1] Annex I Part I under the conditions identified in annex A.
Different use cases representing different product architecture are presented in clause 4.6. Requirements applicability in
clause 5 then defines which requirements apply to which use case to ensure compliance with the CRA's essential
cybersecurity requirements.
2 References
2.1 Normative references
References are either specific (identified by date of publication and/or edition number or version number) or
non-specific. For specific references, only the cited version applies. For non-specific references, the latest version of the
referenced document (including any amendments) applies.
Referenced documents which are not found to be publicly available in the expected location might be found in the
ETSI docbox.
NOTE: While any hyperlinks included in this clause were valid at the time of publication, ETSI cannot guarantee
their long-term validity.
The following referenced documents are necessary for the application of the present document.
[1] ENISA Report 1747792503: "European Cybersecurity Certification Group Sub-group on
Cryptography Agreed Cryptographic Mechanisms - version 2" – April 2025.
[2] Recommendation ITU-T X.509 (10/2019): "Information technology - Open Systems
Interconnection - The Directory: Public-key and attribute certificate frameworks".
NOTE: Identical text in the defining of public-key and attribute certificates is also available in ISO/IEC 9594‑8
(paywall).
[3] IEEE Std 1609.2™-2025" "(2025): "Standard for Wireless Access in Vehicular Environments -
Security Services for Applications and Management Messages".
[4] IETF RFC 6960 (June 2013): "X.509 Internet Public Key Infrastructure Online Certificate Status
Protocol - OCSP".
2.2 Informative references
References are either specific (identified by date of publication and/or edition number or version number) or
nonspecific. For specific references, only the cited version applies. For non-specific references, the latest version of the
referenced document (including any amendments) applies.
ETSI
10 Draft ETSI EN 304 624 V1.0.0 (2026-08)
NOTE: While any hyperlinks included in this clause were valid at the time of publication, ETSI cannot guarantee
their long term validity.
The following referenced documents may be useful in implementing an ETSI deliverable or add to the reader's
understanding but are not required for conformance to the present document.
[i.1] Regulation (EU) 2024/2847 of the European Parliament and of the Council of 23 October 2024 on
horizontal cybersecurity requirements for products with digital elements and amending
Regulations (EU) No 168/2013 and (EU) 2019/1020 and Directive (EU) 2020/1828 (Cyber
Resilience Act).
[i.2] Commission Implementing Regulation (EU) 2025/2392 of 28 November 2025 on the technical
description of the categories of important and critical products with digital elements pursuant to
Regulation (EU) 2024/2847 of the European Parliament and of the Council.
[i.3] Standardisation request M/606 - C(2025)618: "Commission Implementing decision of 3.2.2025 on
...